

Understanding switchport modes is fundamental to VLAN configuration on Cisco Catalyst switches. Each mode determines how a port handles frames, which VLANs are allowed on the port, and how the switch negotiates with neighboring devices. This article explains the four switchport modes and shows you when and why to use each one.
New to VLAN? Start with the full VLAN and Layer 2 switching guide, then come back here for the deep dive.
Switchport Modes Overview
A switchport can operate in one of four modes, each with a specific purpose:
- Access mode: Port handles traffic for a single VLAN only
- Trunk mode: Port handles traffic for multiple VLANs simultaneously
- Dynamic auto: Port negotiates with neighbor to become trunk or access
- Dynamic desirable: Port actively negotiates to become trunk if possible
Most production networks use access or static trunk modes; dynamic modes are legacy negotiation mechanisms that create security and operational issues.
Access Mode: Single VLAN per Port
Access mode is the simplest and most common switchport mode. An access port carries traffic for exactly one VLAN. All frames received on an access port are assumed to belong to that VLAN, and all frames transmitted on the port are untagged (no 802.1Q header):
About the ACC-SW1 examples: the ACC-SW1 configuration and output that use GigabitEthernet1/0/x ports, in this section and in the trunk, DTP and troubleshooting sections below, are illustrative. They show Catalyst 9300-style port names and were not captured from a lab, because the virtual switches in my home lab have no Gi1/0/x ports. The DTP results in "Lab: DTP Results from Both Ends" are real captures from IOSv-L2.
! Illustrative example (Catalyst Gi1/0/x naming), not a lab capture
ACC-SW1# configure terminal
ACC-SW1(config)# interface GigabitEthernet 1/0/1
ACC-SW1(config-if)# switchport mode access
ACC-SW1(config-if)# switchport access vlan 10
ACC-SW1(config-if)# description Users-Workstation-1
ACC-SW1(config-if)# no shutdown
ACC-SW1(config-if)# end
When a host on a workstation sends an Ethernet frame to the switch on this port, the switch receives an untagged frame and internally tags it as VLAN 10. When the switch forwards the frame internally, it uses the VLAN tag to route it to other ports in VLAN 10. When forwarding the frame out another access port in VLAN 10, the switch removes the tag before transmitting.
Access Mode Behavior with Multiple VLANs
If you attempt to receive tagged frames on an access port, the switch drops them by default. This is a safety feature:
! Illustrative example (Catalyst Gi1/0/x naming), not a lab capture
! A trunk link sends tagged frames. If an access port receives them,
! they are dropped because the port doesn't understand 802.1Q.

ACC-SW1# show interfaces GigabitEthernet 1/0/1 switchport

Name: Gi1/0/1
Switchport: Enabled
Administrative Mode: static access
Operational Mode: static access
Access Mode VLAN: 10 (Users)
Trunking Native Mode VLAN: 1 (default)
The "Trunking Native Mode VLAN" field still exists in access mode. This is where tagged frames with no VLAN tag (or a tag matching the native VLAN on a trunk) would be assigned. In access mode, this is primarily informational and does not affect port behavior.
Trunk Mode: Multiple VLANs per Port
Trunk mode allows a single physical link to carry traffic for multiple VLANs simultaneously. Each frame on the trunk is tagged with a 4-byte 802.1Q header identifying which VLAN it belongs to. Trunks are used between switches, not to end hosts (except in rare multi-VLAN scenarios):
! Illustrative example (Catalyst Gi1/0/x naming), not a lab capture
ACC-SW1# configure terminal
ACC-SW1(config)# interface GigabitEthernet 1/0/23
ACC-SW1(config-if)# switchport mode trunk
ACC-SW1(config-if)# switchport trunk encapsulation dot1q
ACC-SW1(config-if)# switchport trunk allowed vlan 10,20,30,40,50,99
ACC-SW1(config-if)# switchport trunk native vlan 99
ACC-SW1(config-if)# description Trunk-to-DIST-SW1
ACC-SW1(config-if)# no shutdown
ACC-SW1(config-if)# end
On a trunk, frames are always tagged with a VLAN ID except for frames in the native VLAN, which are transmitted untagged. This is a critical detail for troubleshooting.
Trunk Configuration Elements
switchport trunk encapsulation:
The encapsulation command specifies which tagging protocol to use. Modern Catalyst switches support only dot1q (802.1Q); ISL (Inter-Switch Link) was Cisco's proprietary protocol and is no longer supported on Catalyst 9000 series. On older platforms that support both, you must explicitly configure dot1q:
! Illustrative example (Catalyst Gi1/0/x naming), not a lab capture
ACC-SW1(config-if)# switchport trunk encapsulation dot1q
switchport trunk allowed vlan:
This command specifies which VLANs are permitted to traverse the trunk. VLANs not in this list are pruned (not sent) on the trunk:
! Illustrative example (Catalyst Gi1/0/x naming), not a lab capture
ACC-SW1(config-if)# switchport trunk allowed vlan 10,20,30,40,50,99
Only VLAN traffic in this list crosses the trunk link. This reduces bandwidth waste and prevents unintended VLAN communication.
switchport trunk native vlan:
The native VLAN is special on trunks. Frames in the native VLAN are transmitted untagged (no 802.1Q header). This historical design originated when devices didn't support 802.1Q tagging. Modern production networks change the native VLAN from the default (VLAN 1) to an unused VLAN like VLAN 99:
! Illustrative example (Catalyst Gi1/0/x naming), not a lab capture
ACC-SW1(config-if)# switchport trunk native vlan 99
Why change native VLAN? VLAN 1 is the default management VLAN on all switches. If the native VLAN is VLAN 1, an attacker could theoretically craft untagged frames to reach management functions on neighboring switches. By changing the native VLAN to an unused VLAN (99 in our topology), you eliminate this attack vector.
Verifying Trunk Configuration
The show interfaces trunk command displays trunk-specific information:
! Illustrative example (Catalyst Gi1/0/x naming), not a lab capture
ACC-SW1# show interfaces trunk

Port        Mode         Encapsulation  Status        Native vlan
Gi1/0/23    on           802.1q         trunking      99

Port        Vlans allowed on trunk
Gi1/0/23    10,20,30,40,50,99

Port        Vlans allowed and active in management domain
Gi1/0/23    10,20,30,40,50,99

Port        Vlans in spanning-tree forwarding state and not pruned
Gi1/0/23    10,20,30,40,50,99
Each line provides specific information:
- Mode on: The port is in trunk mode
- Encapsulation 802.1q: Uses 802.1Q tagging
- Status trunking: The link is up and operational
- Native vlan 99: Untagged frames belong to VLAN 99
- Vlans allowed: Which VLANs are permitted on the trunk
- Vlans allowed and active: Which allowed VLANs actually exist on the switch
- Vlans in spanning-tree forwarding state: Which VLANs are not blocked by Spanning Tree Protocol
Dynamic Trunking Protocol (DTP): Negotiation Fundamentals
Dynamic Trunking Protocol (DTP) is a Cisco proprietary protocol that allows switches to automatically negotiate whether a link should be a trunk or an access port. Three commands control DTP behavior:
switchport mode dynamic auto
A port in dynamic auto mode will become a trunk only if the neighboring port is configured as: - switchport mode trunk - switchport mode dynamic desirable
Otherwise, it remains in access mode:
! Illustrative example (Catalyst Gi1/0/x naming), not a lab capture
ACC-SW1# configure terminal
ACC-SW1(config)# interface GigabitEthernet 1/0/24
ACC-SW1(config-if)# switchport mode dynamic auto
ACC-SW1(config-if)# end

! If Gi1/0/24 on ACC-SW1 connects to Gi1/0/23 on DIST-SW1
! and Gi1/0/23 is configured with 'switchport mode trunk',
! the link will become a trunk.
switchport mode dynamic desirable
A port in dynamic desirable mode actively negotiates to become a trunk. It will become a trunk if the neighbor is: - switchport mode trunk - switchport mode dynamic auto - switchport mode dynamic desirable
! Illustrative example (Catalyst Gi1/0/x naming), not a lab capture
ACC-SW1# configure terminal
ACC-SW1(config)# interface GigabitEthernet 1/0/24
ACC-SW1(config-if)# switchport mode dynamic desirable
ACC-SW1(config-if)# end
Negotiation Matrix
Read each card below as the local port's operational mode. The trunk/access entries describe different ends of the same mismatch: the static trunk end stays trunk, while the access end stays access. They do not mean that the two ends formed a matched trunk. The captured lab below shows both ends and includes static trunk with switchport nonegotiate.
Why Static Configuration is Best Practice
Although DTP allows automatic negotiation, production networks universally disable it and use static trunk configuration:
! Illustrative example (Catalyst Gi1/0/x naming), not a lab capture
! Disable DTP on a specific port
ACC-SW1(config)# interface GigabitEthernet 1/0/23
ACC-SW1(config-if)# switchport nonegotiate
ACC-SW1(config-if)# end
Reasons to avoid DTP:
- Unpredictable behavior: A misconfiguration on one switch can cause an entire link to change modes unexpectedly
- Security risk: An attacker who gains access to the network could change a device's DTP mode to create unauthorized trunks
- Operational clarity: Static configurations are visible in running-config and are easier to audit
- Troubleshooting simplicity: A link is either a trunk or access by explicit configuration, not by negotiation outcome
- No benefit: Modern networks use orchestration and infrastructure-as-code; automatic negotiation provides no operational value
Lab: DTP Results from Both Ends
I built this lab in my home lab on Cisco IOSv-L2, Experimental Version 15.2(20200924:215240), with Linux hosts in Containerlab. A fresh SW2 Gi1/2 reported administrative mode dynamic auto, operational mode static access, and negotiation On before configuration. That is the observed default of this image; check a fresh port on your own model rather than assuming every Catalyst ships with it.
Port map, confirmed in a rerun on October 20, 2026: on both switches Gi0/1 is the main SW1-SW2 dot1q trunk (native VLAN 99, allowed 10,20,99, negotiation off), Gi0/2 and Gi0/3 are the two DTP test links, Gi1/0 is an access port in VLAN 10 (h10a on SW1, h10b on SW2) and Gi1/1 is an access port in VLAN 20 (h20a, h20b). SW2 also has Gi1/2, a static trunk to a Linux host carrying tagged VLANs 10 and 20 with VLAN 99 untagged. SW1 has no Gi1/2. Gi0/0 on both is the Containerlab management port.
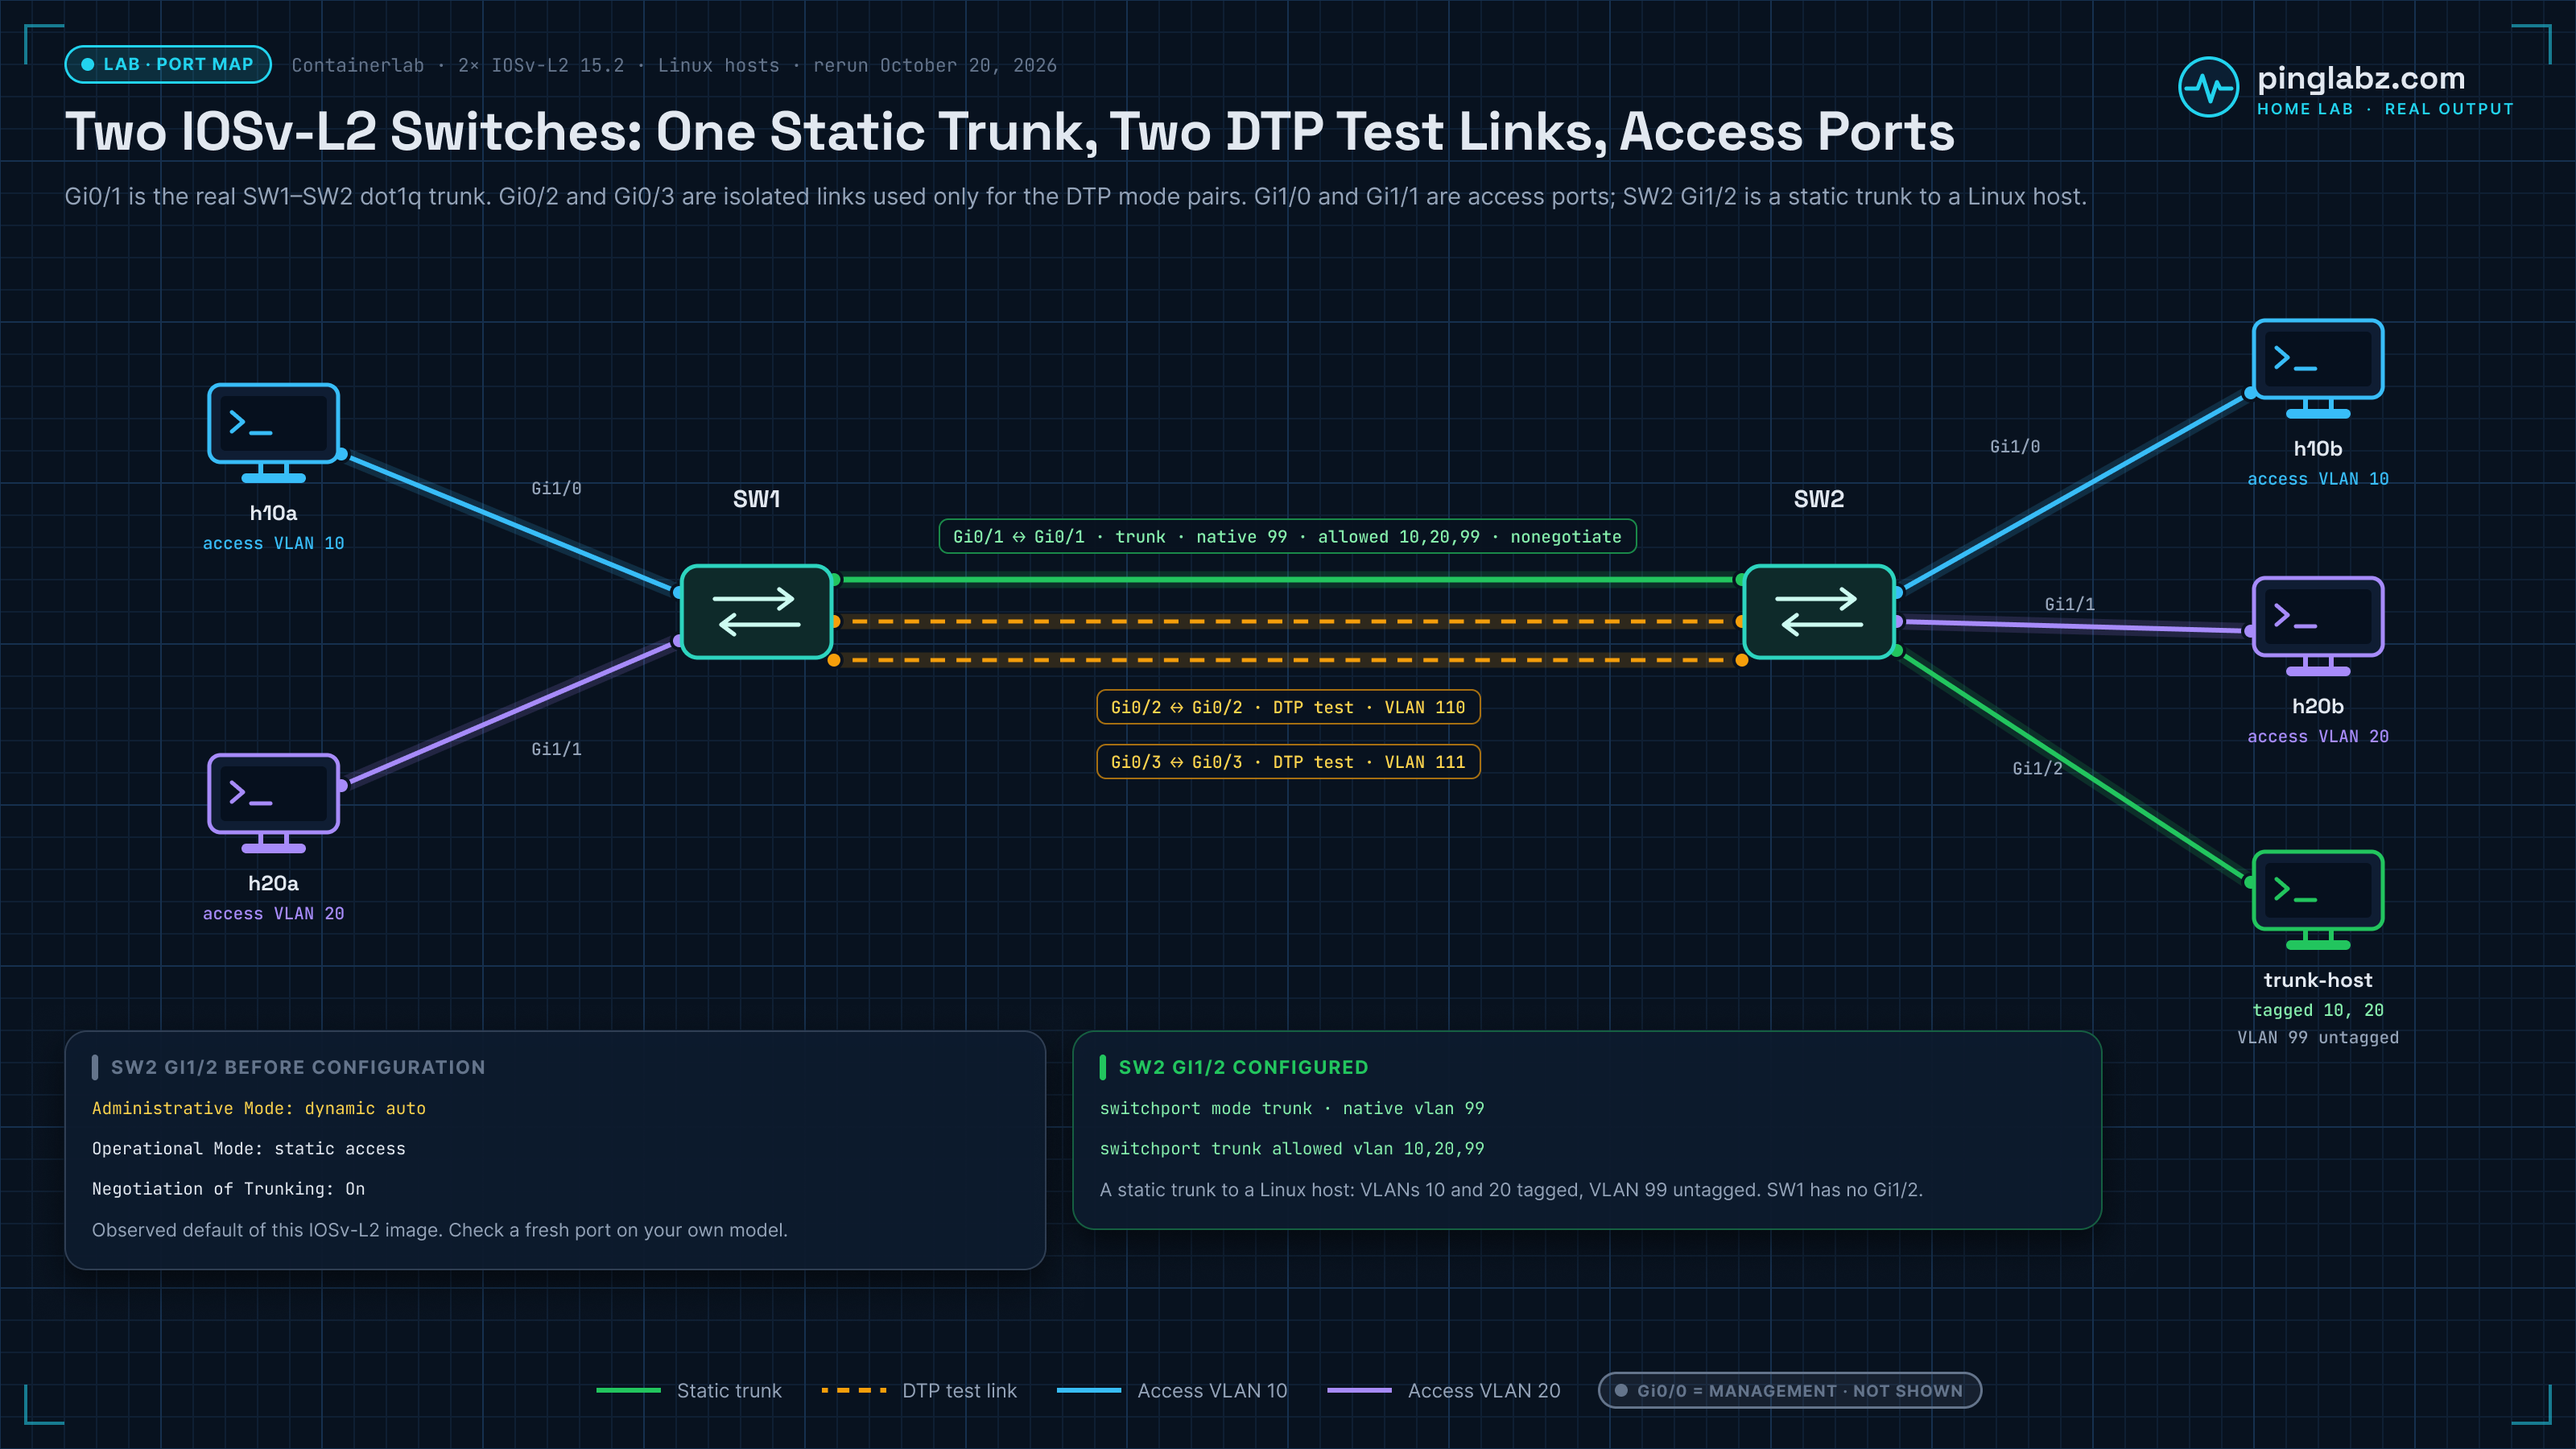
Two isolated links connected SW1 to SW2: Gi0/2 used VLAN 110 and Gi0/3 used VLAN 111. Before each test, both ports were shut, the previous negotiation setting was cleared, and access mode supplied a known starting point. After applying each pair and bringing the ports up, the test waited 45 seconds before collecting both ends. The table comes from the captured Operational Mode and Negotiation of Trunking fields.
All Captured Mode Pairs
trunk + nonegotiate means both switchport mode trunk and switchport nonegotiate. “Static access” and “trunk” below are the actual operational labels, not predictions of whether traffic should pass.
| SW1 configured | SW2 configured | SW1 operational | SW2 operational | Negotiation SW1 / SW2 |
|---|---|---|---|---|
| access | access | static access | static access | Off / Off |
| access | trunk | static access | trunk | Off / On |
| access | dynamic auto | static access | static access | Off / On |
| access | dynamic desirable | static access | static access | Off / On |
| access | trunk + nonegotiate | static access | trunk | Off / Off |
| trunk | trunk | trunk | trunk | On / On |
| trunk | dynamic auto | trunk | trunk | On / On |
| trunk | dynamic desirable | trunk | trunk | On / On |
| trunk | trunk + nonegotiate | trunk | trunk | On / Off |
| dynamic auto | dynamic auto | static access | static access | On / On |
| dynamic auto | dynamic desirable | trunk | trunk | On / On |
| dynamic auto | trunk + nonegotiate | static access | trunk | On / Off |
| dynamic desirable | dynamic desirable | trunk | trunk | On / On |
| dynamic desirable | trunk + nonegotiate | static access | trunk | On / Off |
| trunk + nonegotiate | trunk + nonegotiate | trunk | trunk | Off / Off |
Two additional reversed-direction checks agreed with the corresponding pairs:
| SW1 configured | SW2 configured | SW1 operational | SW2 operational | Negotiation SW1 / SW2 |
|---|---|---|---|---|
| dynamic auto | trunk | trunk | trunk | On / On |
| trunk + nonegotiate | dynamic auto | trunk | static access | Off / On |
The lab captured the 15 distinct pairs plus those two reversals. It did not repeat every pair in both orientations. A static trunk with negotiation disabled stayed trunk locally, but neither auto nor desirable became trunk against that silent neighbor.
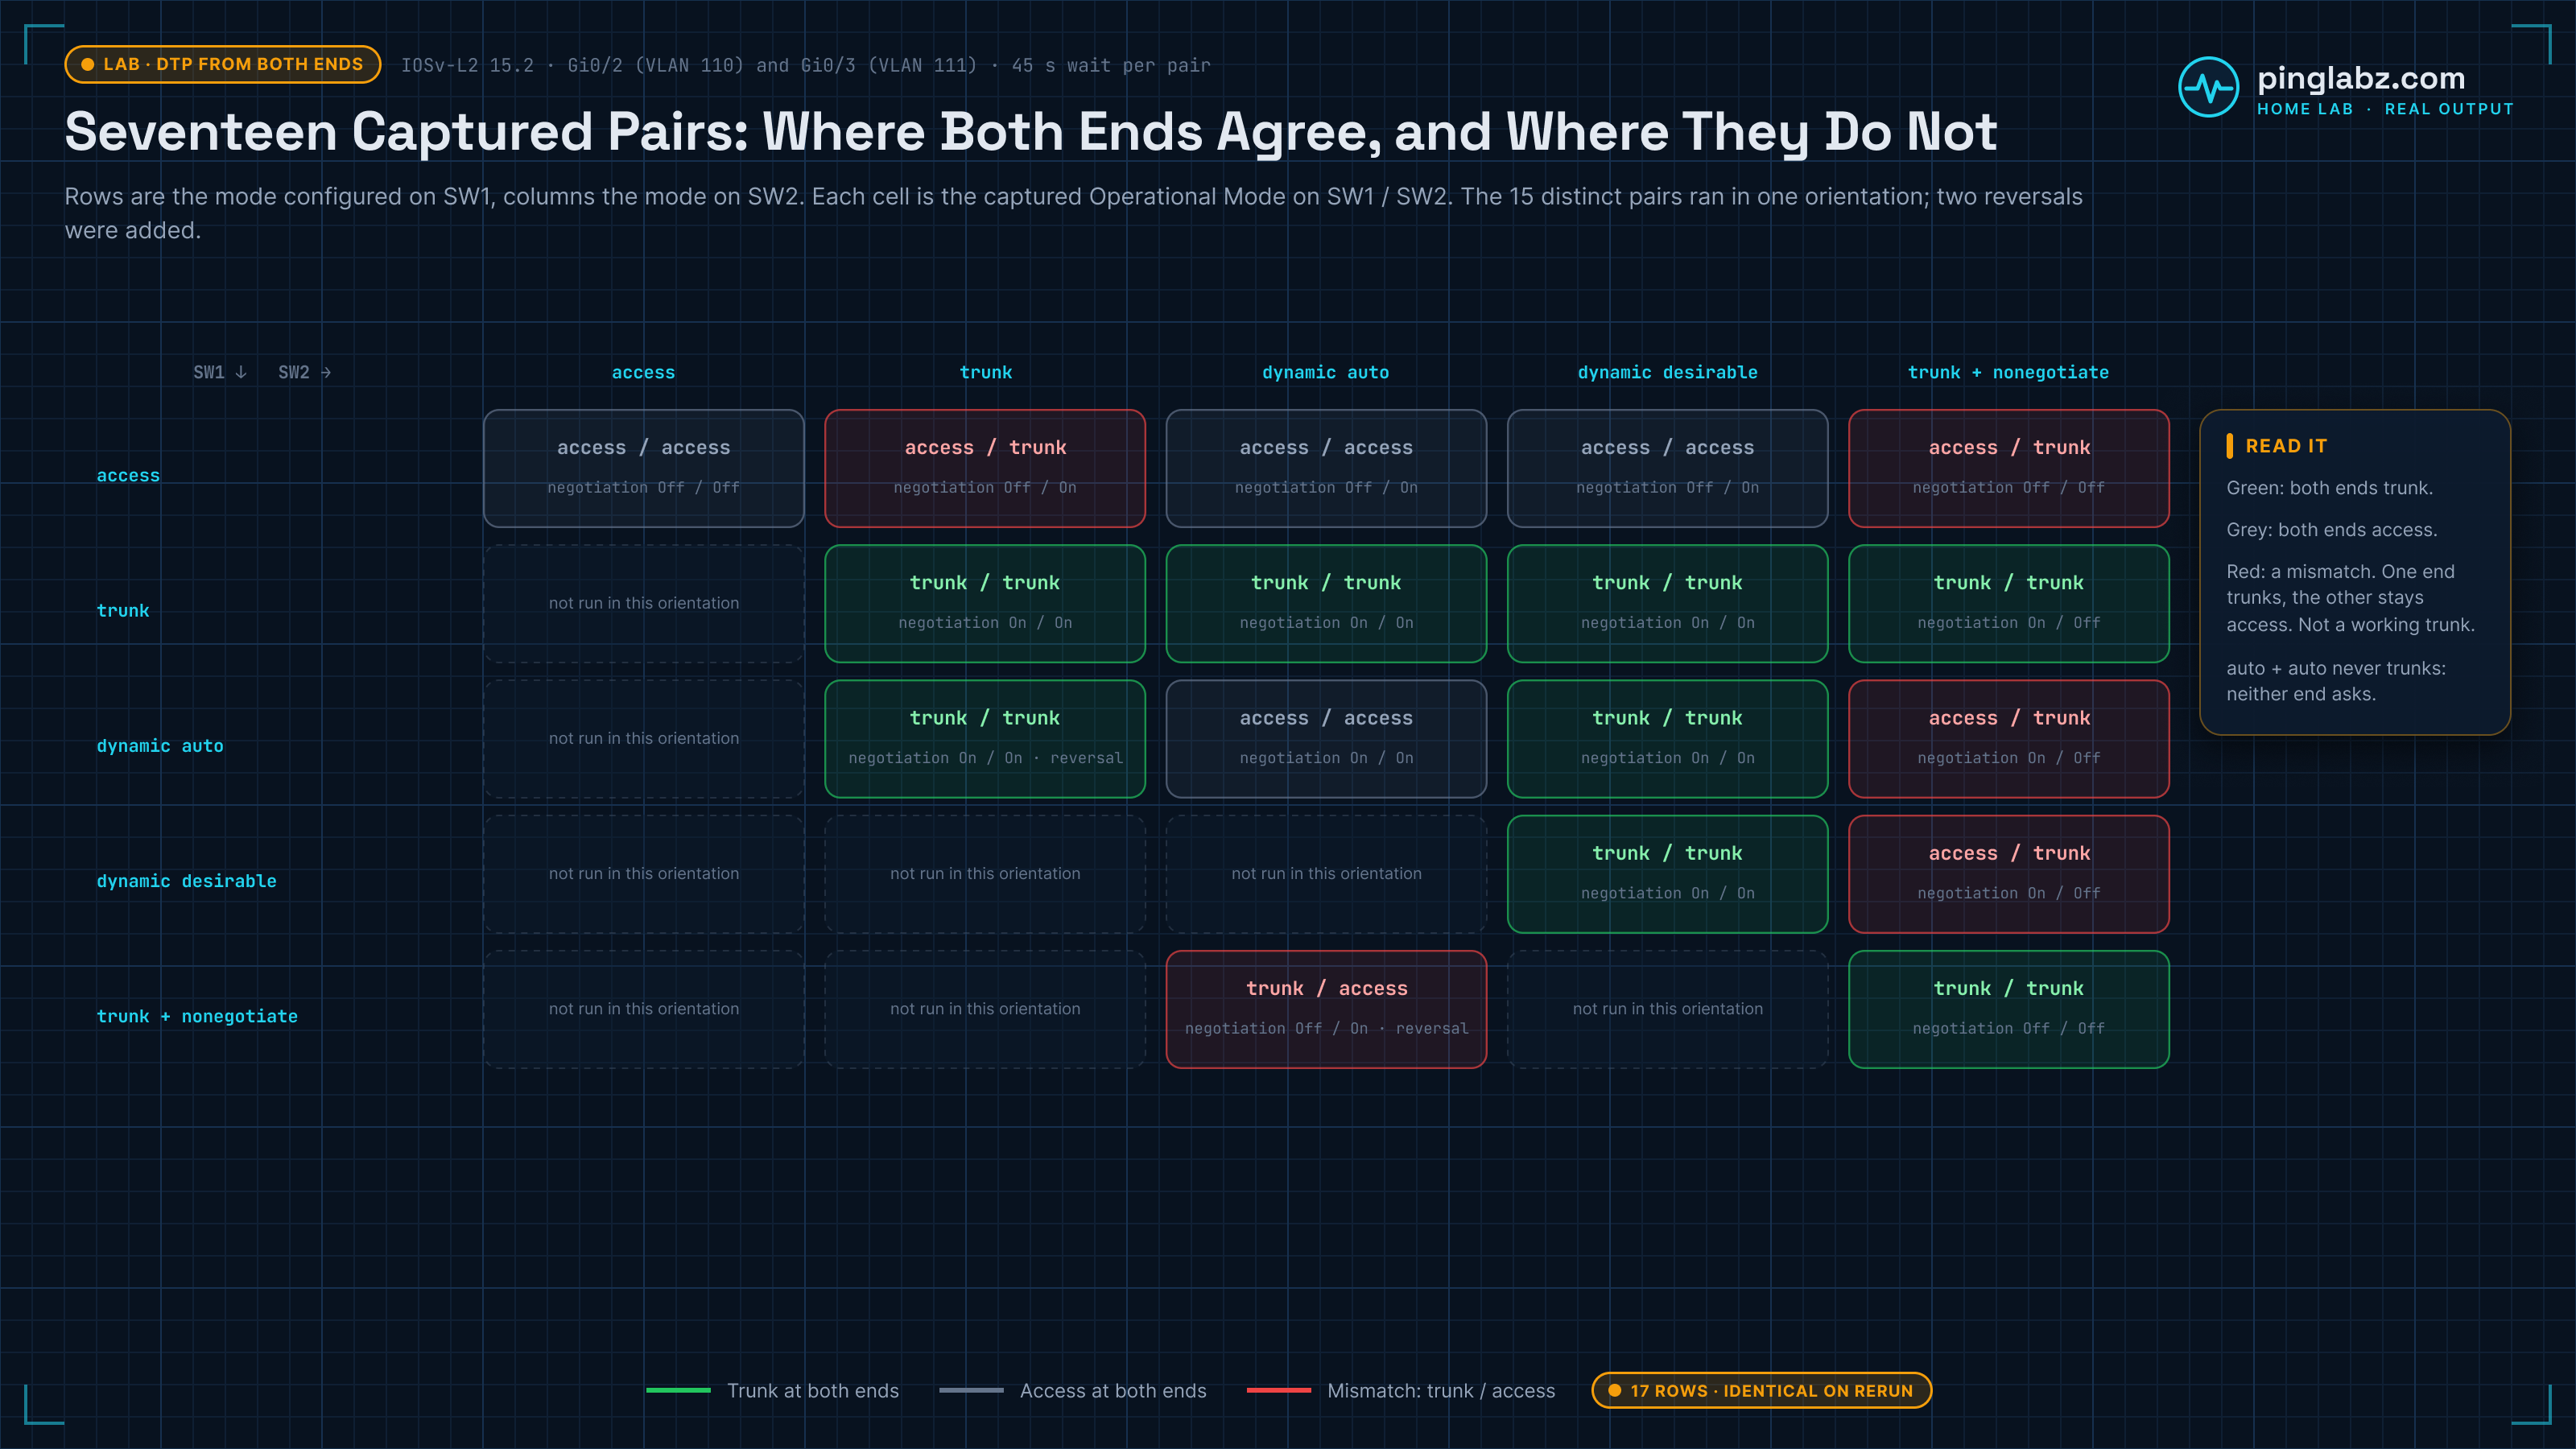
I reran the full matrix on the same IOSv-L2 image, and all 17 rows above came out identical, cell for cell. A short cross-check on IOL-L2 (IOS XE 17.18.2) agreed for auto/auto, auto/desirable and auto against trunk plus nonegotiate. One IOL-L2 difference: its ports default to switchport trunk encapsulation negotiate, so auto/desirable negotiated ISL, and switchport mode trunk was rejected until I set switchport trunk encapsulation dot1q.
Auto + Auto: Neither End Starts a Trunk
On SW1, the auto/auto test used Gi0/3:
...
SW1#show interfaces GigabitEthernet0/3 switchport
Name: Gi0/3
Switchport: Enabled
Administrative Mode: dynamic auto
Operational Mode: static access
Administrative Trunking Encapsulation: dot1q
Operational Trunking Encapsulation: native
Negotiation of Trunking: On
Access Mode VLAN: 111 (VLAN0111)
...
SW2 reported the same result:
...
SW2#show interfaces GigabitEthernet0/3 switchport
Name: Gi0/3
Switchport: Enabled
Administrative Mode: dynamic auto
Operational Mode: static access
Administrative Trunking Encapsulation: dot1q
Operational Trunking Encapsulation: native
Negotiation of Trunking: On
Access Mode VLAN: 111 (VLAN0111)
...
Auto + Desirable: Both Ends Become Trunks
On Gi0/2, SW1 was auto and SW2 was desirable:
...
SW1#show interfaces GigabitEthernet0/2 switchport
Name: Gi0/2
Switchport: Enabled
Administrative Mode: dynamic auto
Operational Mode: trunk
Administrative Trunking Encapsulation: dot1q
Operational Trunking Encapsulation: dot1q
Negotiation of Trunking: On
Access Mode VLAN: 110 (VLAN0110)
...
...
SW2#show interfaces GigabitEthernet0/2 switchport
Name: Gi0/2
Switchport: Enabled
Administrative Mode: dynamic desirable
Operational Mode: trunk
Administrative Trunking Encapsulation: dot1q
Operational Trunking Encapsulation: dot1q
Negotiation of Trunking: On
Access Mode VLAN: 110 (VLAN0110)
...SW1 also reported a trunk DTP state and received negotiation packets:
...
SW1#show dtp interface GigabitEthernet0/2
DTP information for GigabitEthernet0/2:
  TOS/TAS/TNS:                              TRUNK/AUTO/TRUNK
  TOT/TAT/TNT:                              802.1Q/802.1Q/802.1Q
...
  FSM state:                                S6:TRUNK
  # times multi & trunk                     0
...
  Statistics
  ----------
  4 packets received (4 good)
  0 packets dropped
...
Its trunk list included Gi0/2 and VLAN 110. The other test link, Gi0/3, was absent on SW1:
...
SW1#show interfaces trunk

Port        Mode             Encapsulation  Status        Native vlan
Gi0/1       on               802.1q         trunking      99
Gi0/2       auto             802.1q         trunking      110

Port        Vlans allowed on trunk
Gi0/1       10,20,99
Gi0/2       110

Port        Vlans allowed and active in management domain
Gi0/1       10,20,99
Gi0/2       110

Port        Vlans in spanning tree forwarding state and not pruned
Gi0/1       10,20,99
Gi0/2       110
...
The separate frame capture for this auto/desirable link identified Cisco SNAP DTP to 01:00:0c:cc:cc:cc. That multicast destination also carried other Cisco protocols, so the destination MAC alone is not proof that a frame is DTP.
Nonegotiate + Dynamic: Check Both Ends
In the same round, Gi0/3 paired auto on SW1 with static trunk plus nonegotiate on SW2:
...
SW1#show interfaces GigabitEthernet0/3 switchport
Name: Gi0/3
Switchport: Enabled
Administrative Mode: dynamic auto
Operational Mode: static access
Administrative Trunking Encapsulation: dot1q
Operational Trunking Encapsulation: native
Negotiation of Trunking: On
Access Mode VLAN: 111 (VLAN0111)
...
...
SW2#show interfaces GigabitEthernet0/3 switchport
Name: Gi0/3
Switchport: Enabled
Administrative Mode: trunk
Operational Mode: trunk
Administrative Trunking Encapsulation: dot1q
Operational Trunking Encapsulation: dot1q
Negotiation of Trunking: Off
Access Mode VLAN: 111 (VLAN0111)
...SW2 listed Gi0/3 as trunking, while SW1 did not. The desirable/nonegotiate pair in the next round had the same split result. One switch's show interfaces trunk is therefore only half the check.
For an intended static trunk, configure trunk mode at both ends, agree on native and allowed VLANs, and disable negotiation at both ends. Then verify the operational state on both switches. Use tagged and untagged packet captures to check the resulting frame format; use the SVI diagnosis if the VLAN gateway remains unreachable.
Access vs. Trunk: Decision Tree
Use this decision tree to determine the correct switchport mode:
Is this link connecting to an end host (server, workstation, IP phone, printer)? - Yes → Use switchport mode access + switchport access vlan <id> - No → Continue
Is this link connecting to another switch? - Yes, and multiple VLANs need to cross the link → Use switchport mode trunk + switchport nonegotiate - Yes, and only one VLAN needs to cross → Use switchport mode access (unusual but valid) - No → Use access mode
Verification and Troubleshooting
Symptom: Link should be trunk but is in access mode
Cause: The port was configured with switchport mode access or with dynamic modes that resulted in access mode negotiation.
Fix: Explicitly configure the port as trunk:
! Illustrative example (Catalyst Gi1/0/x naming), not a lab capture
ACC-SW1# configure terminal
ACC-SW1(config)# interface GigabitEthernet 1/0/23
ACC-SW1(config-if)# switchport mode trunk
ACC-SW1(config-if)# switchport nonegotiate
ACC-SW1(config-if)# end

ACC-SW1# show interfaces GigabitEthernet 1/0/23 switchport | include Mode

Administrative Mode: static trunk
Operational Mode: trunk
Symptom: Unexpected frames received on access port
Cause: A neighboring device sent tagged frames (802.1Q) to an access port, or a trunk port sent untagged frames that don't match the native VLAN.
Fix: Verify the neighboring port is in the correct mode:
! Illustrative example (Catalyst Gi1/0/x naming), not a lab capture
ACC-SW1# show interfaces GigabitEthernet 1/0/23 switchport | include Mode

Administrative Mode: static access

! If this should be a trunk, reconfigure it
ACC-SW1(config-if)# switchport mode trunk
ACC-SW1(config-if)# switchport nonegotiate
Symptom: DTP negotiation unstable (link flaps between trunk and access)
Cause: DTP is enabled and the neighbor's configuration is incompatible with the DTP negotiation matrix.
Fix: Cisco IOS has no global command that turns DTP off, so disable it per link. Configure static trunks on every switch-to-switch link with switchport nonegotiate at both ends, and use switchport mode access on host ports (in the lab below, access ports reported Negotiation of Trunking: Off):
! Illustrative example (Catalyst Gi1/0/x naming), not a lab capture
! On each switch-to-switch link (both ends)
ACC-SW1(config)# interface GigabitEthernet 1/0/23
ACC-SW1(config-if)# switchport mode trunk
ACC-SW1(config-if)# switchport trunk allowed vlan 10,20,30,40,50,99
ACC-SW1(config-if)# switchport trunk native vlan 99
ACC-SW1(config-if)# switchport nonegotiate
ACC-SW1(config-if)# end
Key Takeaways
- Access mode is for end hosts; each port carries one VLAN without 802.1Q tagging
- Trunk mode carries multiple VLANs on a single link using 802.1Q tagging
- Dynamic modes (auto/desirable) use DTP to negotiate but are rarely used in production due to complexity and security concerns
- Always use
switchport nonegotiatewith trunk mode to disable DTP and prevent unexpected mode changes - Change the native VLAN from default (VLAN 1) to an unused VLAN (like VLAN 99) for security
- Verify switchport configuration with
show interfaces switchport(for access ports) andshow interfaces trunk(for trunks)