

Updated October 2026: I re-tested private VLANs on IOL-L2 17.18.2 in my home lab (VTP transparent required), including a promiscuous-mapping fault that cut gateway reachability. Platform show-command and secondary-VLAN nuances are in the new section before Key Takeaways.
The Micro-Segmentation Problem
You have 50 servers in a hosted environment, all on the same VLAN, all reaching the same gateway. But you don't want them talking to each other, only to the firewall or router. VLAN access lists can do it, but they get complex at scale. Private VLANs solve this on the switch at Layer 2, by dividing a primary VLAN into isolated and community secondary VLANs. (My lab used virtual switches, so hardware forwarding performance was not tested.)
(This article is part of the PingLabz VLAN series - the full VLAN and Layer 2 switching guide maps the whole cluster in reading order.)
Private VLAN Fundamentals
Private VLANs (PVLANs) subdivide a primary VLAN into secondary VLANs, each with specific communication rules:
- Primary VLAN: The parent VLAN. In my lab, VLAN 100 is the primary.
- Isolated Secondary VLAN: Hosts here cannot talk to each other. Only upstream to promiscuous ports.
- Community Secondary VLAN: Hosts within the community can talk to each other, but not to other communities or isolated hosts. (My lab had one community host, so same-community peer traffic was not tested.)
- Promiscuous Port: Connected to a router, firewall, or gateway. Sees all traffic in the primary VLAN and can reach any secondary.
The real power: all these secondary VLANs share a single gateway IP on the primary VLAN, and the switch's private VLAN policy, not separate VLANs and subnets, keeps hosts apart. In my lab that held for ICMP; captures still showed some ARP and other frames reaching isolated hosts, so do not treat it as full frame confidentiality.
Configuration on SW1
This is the configuration from my home lab on an IOL-L2 17.18.2 switch, SW1: VLAN 100 primary, VLAN 101 isolated, VLAN 102 community. Hosts A (10.146.0.11) and B (10.146.0.12) sit on isolated ports Ethernet0/2 and Ethernet0/3, host C (10.146.0.13) on community port Ethernet1/0, and router R1 (10.146.0.1) on promiscuous port Ethernet0/1, all in 10.146.0.0/24. The code blocks show the commands exactly as I entered them.
Step 1: Define the Primary VLAN
vtp mode transparent
Setting device to VTP Transparent mode for VLANS.
vlan 100
private-vlan primary
exit
This marks VLAN 100 as a private VLAN primary. vtp mode transparent has to come first: on IOL-L2 17.18.2 (and IOSv-L2 in a parser probe), private-vlan primary was rejected until the switch was in VTP transparent mode:
%Private VLANs can only be configured when VTP is in transparent/off modes in VTP version 1 or 2 and in server/transparent/off modes in VTP version 3 when pruning is turned offStep 2: Define the Secondary VLANs
vlan 101
private-vlan isolated
exit
vlan 102
private-vlan community
exit
VLAN 101 is the isolated secondary; VLAN 102 is the community secondary. A secondary does nothing useful until it is associated with a primary, but it can exist without one: in my lab I created VLAN 103 (isolated) and VLAN 104 (community) with no association, and show vlan private-vlan listed both with primary none. I then removed them.
Step 3: Associate Secondary VLANs with the Primary
vlan 100
private-vlan association 101,102
exit
This binds the secondary VLANs to the primary. Now the primary VLAN "knows" about them.
Step 4: Configure Isolated Ports
Ethernet0/2 (host A, 10.146.0.11) and Ethernet0/3 (host B, 10.146.0.12) are isolated hosts, for example customer servers that should never communicate with each other:
interface Ethernet0/2
switchport mode private-vlan host
switchport private-vlan host-association 100 101
no shutdown
exit
interface Ethernet0/3
switchport mode private-vlan host
switchport private-vlan host-association 100 101
no shutdown
exit
switchport private-vlan host-association <primary> <secondary> ties the port to the primary and its secondary VLAN.
Step 5: Configure Community Ports
Ethernet1/0 (host C, 10.146.0.13) is a community host, for example a web server in a customer tier. A second community host is configured the same way; I had only one in this lab, so same-community peer traffic was not tested:
interface Ethernet1/0
switchport mode private-vlan host
switchport private-vlan host-association 100 102
no shutdown
exit
Step 6: Configure the Promiscuous Port
Ethernet0/1 (to R1, 10.146.0.1) is the promiscuous port and must be able to see all secondary VLANs:
interface Ethernet0/1
switchport mode private-vlan promiscuous
switchport private-vlan mapping 100 101,102
no shutdown
exit
end
The switchport private-vlan mapping 100 101,102 command tells the port it's in the primary VLAN and can reach secondary VLANs 101 and 102.
Full Configuration Block for SW1
For reference, here is the PVLAN part of SW1's running config from the lab. Note that the switch stores the mapping as 101-102:
vtp mode transparent
!
vlan 100
  private-vlan primary
  private-vlan association 101,102
!
vlan 101
  private-vlan isolated
!
vlan 102
  private-vlan community
!
interface Ethernet0/1
 switchport private-vlan mapping 100 101-102
 switchport mode private-vlan promiscuous
!
interface Ethernet0/2
 switchport private-vlan host-association 100 101
 switchport mode private-vlan host
!
interface Ethernet0/3
 switchport private-vlan host-association 100 101
 switchport mode private-vlan host
!
interface Ethernet1/0
 switchport private-vlan host-association 100 102
 switchport mode private-vlan host
!
Verification
Show VLAN Private-VLAN Status
show vlan private-vlan

Primary Secondary Type              Ports
------- --------- ----------------- ------------------------------------------
100     101       isolated          Et0/1, Et0/2, Et0/3
100     102       community         Et0/1, Et1/0

SW1#
show vlan private-vlan type

Vlan Type
---- -----------------
100  primary
101  isolated
102  community
Show Port PVLAN Association
On IOL-L2 17.18.2 the bare show interfaces <port> private-vlan is incomplete, and adding mapping returned no information, so use show interfaces <port> switchport. Selected lines from isolated port Et0/2 and promiscuous port Et0/1:
show interfaces Ethernet0/2 private-vlan
% Incomplete command.

show interfaces Ethernet0/1 private-vlan mapping
Private vlan mapping information is not available for Ethernet0/1

show interfaces Ethernet0/2 switchport
Name: Et0/2
Operational Mode: private-vlan host
Administrative private-vlan host-association: 100 (VLAN0100) 101 (VLAN0101)

show interfaces Ethernet0/1 switchport
Name: Et0/1
Operational Mode: private-vlan promiscuous
Administrative private-vlan mapping: 100 (VLAN0100) 101 (VLAN0101) 102 (VLAN0102)
Show VLAN Detail
show vlan id 100

VLAN Name                             Status    Ports
---- -------------------------------- --------- -------------------------------
100  VLAN0100                         active

VLAN Type  SAID       MTU   Parent RingNo BridgeNo Stp  BrdgMode Trans1 Trans2
---- ----- ---------- ----- ------ ------ -------- ---- -------- ------ ------
100  enet  100100     1500  -      -      -        -    -        0      0

Remote SPAN VLAN
----------------
Disabled

Primary Secondary Type              Ports
------- --------- ----------------- ------------------------------------------
100     101       isolated          Et0/1, Et0/2, Et0/3
100     102       community         Et0/1, Et1/0
Troubleshooting
Symptom: Host in Isolated VLAN Cannot Ping Upstream Router
Cause: Promiscuous port not in the correct PVLAN mapping. Fix: Verify the promiscuous port's mapping includes the isolated secondary VLAN. In my lab, removing the mapping on Ethernet0/1 put the port in Operational Mode: down and cut gateway pings for all three hosts; restoring it worked once STP had the port back in forwarding:
interface Ethernet0/1
no switchport private-vlan mapping

show interfaces Ethernet0/1 switchport
Operational Mode: down
Administrative private-vlan mapping: none

interface Ethernet0/1
switchport private-vlan mapping 100 101,102
Symptom: Community Hosts on VLAN 102 Cannot Ping Each Other
Cause: Ports are misconfigured as isolated rather than community. Fix: Check the host association on each port. (With one community host in my lab, I did not reproduce this symptom.)
show interfaces Ethernet1/0 switchport
Administrative private-vlan host-association: 100 (VLAN0100) 102 (VLAN0102)

interface Ethernet1/0
switchport private-vlan host-association 100 102
Symptom: Isolated Host (Et0/2) Can Ping Another Isolated Host (Et0/3)
Cause: Both ports are in the same community VLAN instead of the isolated secondary. Fix: Verify the secondary VLAN association and make sure isolated hosts use the isolated secondary. In my lab the isolated row listed Et0/2 and Et0/3, and A-to-B pings failed 3 of 3 even with B's MAC pinned on A:
show vlan private-vlan
100     101       isolated          Et0/1, Et0/2, Et0/3
Symptom: Port Shows "Suspended" in show vlan private-vlan
Cause: A secondary VLAN has no association to a primary VLAN, or the primary VLAN was deleted. Fix: Re-associate the secondary VLAN or restore the primary. I did not reproduce a suspended state in my lab: unassociated secondaries simply showed primary none.
vlan 100
private-vlan association 101,102
Advanced Configuration: Trunk with PVLAN
PVLANs can traverse trunks if the secondary VLANs are allowed on the trunk. I did not test PVLANs over a trunk in this lab, so treat this as an example, not a verified config:
! Example only, not tested in my lab
interface <trunk-port>
 switchport mode trunk
 switchport trunk allowed vlan 100,101,102
The secondary VLANs must be explicitly allowed. The receiving switch needs identical PVLAN configuration.
Real-World Use Cases
Shared Hosting Provider: Each customer (or customer group) gets isolated ports under one primary VLAN, and all traffic to the internet or shared services flows through a single promiscuous port (the gateway). Customers on isolated ports cannot reach each other directly through the switch. In my lab, pings between isolated hosts failed, but captures still showed some ARP and other frames reaching isolated hosts, so do not rely on PVLANs alone to stop ARP scanning or DoS.
DMZ Design: Servers in a DMZ each need isolation from peer servers but must reach a firewall or gateway. PVLANs can be simpler than separate VLANs per server.
IP Phone Distribution: A community secondary VLAN can connect a group of phones to a cluster of voice gateways (promiscuous port), while isolating each phone from direct peer communication.
Re-tested in my home lab (October 2026)
Built in my home lab with IOL-L2 17.18.2 (SW1), an IOL router R1 as the gateway, and three Alpine Linux hosts on 10.146.0.0/24. Both IOL-L2 and IOSv-L2 exposed the PVLAN CLI, and both needed vtp mode transparent before private-vlan primary would take. Forwarding tests used IOL-L2.
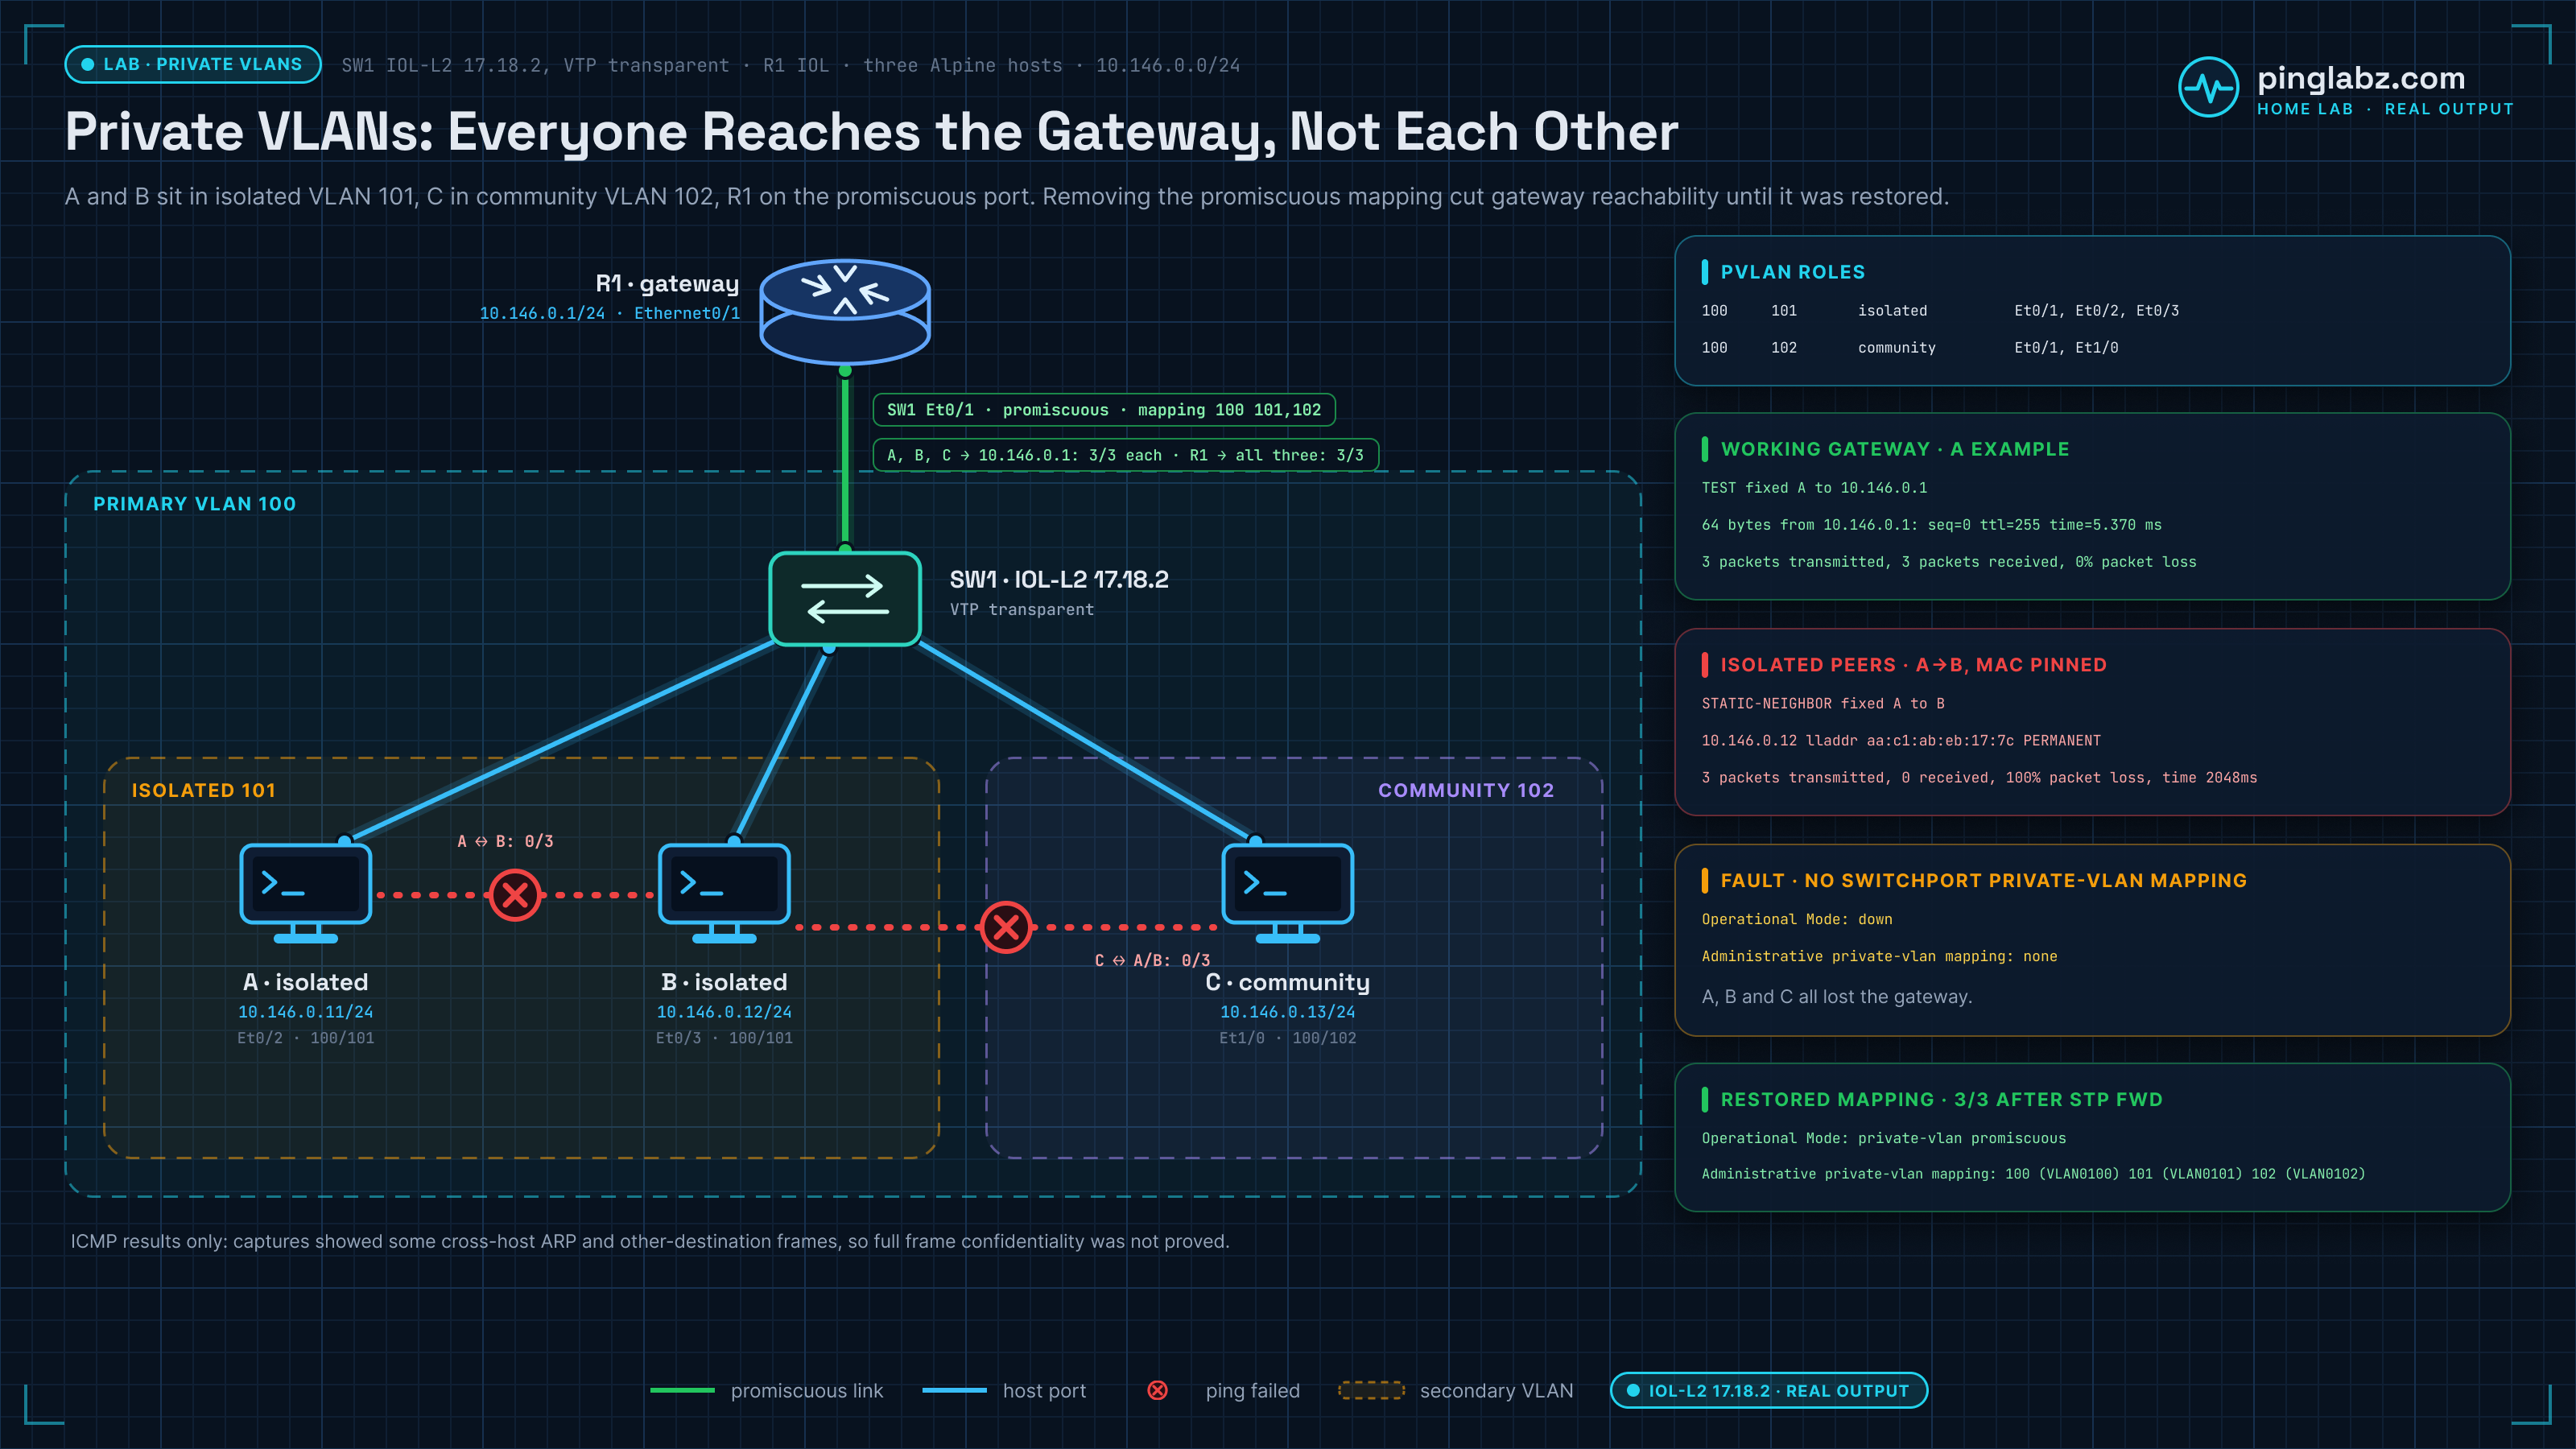
Working baseline
Primary 100 / isolated 101 / community 102 with promiscuous mapping toward R1:
100     101       isolated          Et0/1, Et0/2, Et0/3
100     102       community         Et0/1, Et1/0
Isolated A and B and community C each reached the gateway; peer pings failed even with permanent neighbors:
TEST fixed A to 10.146.0.1
64 bytes from 10.146.0.1: seq=0 ttl=255 time=5.370 ms
3 packets transmitted, 3 packets received, 0% packet loss
STATIC-NEIGHBOR fixed A to B
10.146.0.12 lladdr aa:c1:ab:eb:17:7c PERMANENT
3 packets transmitted, 0 received, 100% packet loss, time 2048msBreak it: remove the promiscuous mapping
no switchport private-vlan mapping on the gateway-facing port dropped operational mode and gateway reachability for all three hosts:
Operational Mode: down
Administrative private-vlan mapping: none
TEST fault A to 10.146.0.1
3 packets transmitted, 0 packets received, 100% packet lossFix: restore the mapping
Restoring switchport private-vlan mapping 100 101,102 brought the port back to promiscuous, and gateway pings recovered 3 of 3 for all three hosts once STP had Et0/1 back in forwarding (FWD):
Operational Mode: private-vlan promiscuous
Administrative private-vlan mapping: 100 (VLAN0100) 101 (VLAN0101) 102 (VLAN0102)

show spanning-tree vlan 100
Et0/1               Desg FWD 100       128.2    P2p
Platform gotchas from the re-test
Bare show interfaces <port> private-vlan is incomplete on IOL-L2, and the mapping suffix returned no information, so use show interfaces <port> switchport:
show interfaces Ethernet0/2 private-vlan
% Incomplete command.
Secondary VLAN definitions can sit with primary none until associated (then removed in the lab):
none 103 isolated Ping failure is not complete frame confidentiality: captures at the isolated hosts still showed some ARP and other-destination frames (for example, isolated host A's capture recorded B's echo requests to C). Same-community peers and PVLAN trunks were not tested in this run.
Key Takeaways
- Private VLANs enforce micro-segmentation at Layer 2 without requiring separate IP subnets per segment or CPU-intensive ACLs.
- Three port types exist: promiscuous (gateway), isolated (no peer-to-peer unicast in our tests), and community (peer-to-peer within group — same-community peers were not re-tested here).
- Secondary VLANs need to be associated with a primary VLAN using
private-vlan associationto be useful; an unassociated secondary can still exist, with primarynone. - Verify with
show vlan private-vlanandshow interfaces <port> switchport. On IOL-L2, bareshow interfaces <port> private-vlanis% Incomplete command.and themappingsuffix returned no information. Configurevtp mode transparentfirst. - Isolation is a Layer-2 policy — we proved ICMP peer failure and gateway reachability on IOL-L2. Captures still saw some ARP/other-destination frames at isolated hosts, so do not oversell complete frame confidentiality. ASIC/wire-speed claims were not tested on virtual images.