

When a dACL is not applying in 802.1X, check three things in order. Does show authentication sessions interface <port> details show an ACS ACL line? Does show ip access-lists list a matching xACSACLx-IP-... ACL marked (per-user)? And did the RADIUS server answer the second request, the one whose User-Name is the ACL name? A missing ACS ACL line with the client fully open usually means aaa authorization network is missing. A port that is Unauthorized right after dot1x Authc Success means the download or the ACL itself failed.
Every output below is from a lab built in my home lab: a Cisco IOSv-L2 15.2 switch, FreeRADIUS 3.0.27 and a Linux client running EAP-TLS with wpa_supplicant 2.11. FreeRADIUS sends the same Cisco AVPairs that ISE sends for a downloadable ACL, so the switch side behaves the same way. I broke the setup five different ways and timed one recovery. New to 802.1X? Start with the 802.1X guide, and for how ISE builds the dACL in the first place see Cisco dACL with ISE and 802.1X.
How dACLs Work: The Download Mechanism
A dACL takes two RADIUS exchanges, and each one can fail on its own:
- Authentication. The Access-Accept for the user carries one AVPair naming the ACL:
ACS:CiscoSecure-Defined-ACL=#ACSACL#-IP-WEB-ONLY-v1. - Download. The switch sends a second Access-Request with that name as the User-Name and
aaa:event=acl-download. The server answers with the ACEs asip:inacl#N=AVPairs.
Here are both exchanges from the FreeRADIUS debug log on a working login:
(6) Sent Access-Accept Id 7 from 192.0.2.11:1812 to 192.0.2.1:1645 length 227
(6)   Cisco-AVPair = "ACS:CiscoSecure-Defined-ACL=#ACSACL#-IP-WEB-ONLY-v1"
(7) Received Access-Request Id 8 from 192.0.2.1:1645 to 192.0.2.11:1812 length 131
(7)   User-Name = "#ACSACL#-IP-WEB-ONLY-v1"
(7) files: users: Matched entry #ACSACL#-IP-WEB-ONLY-v1 at line 4
(7) Sent Access-Accept Id 8 from 192.0.2.11:1812 to 192.0.2.1:1645 length 129
(7)   Cisco-AVPair = "ip:inacl#1=permit tcp any host 203.0.113.80 eq 80"
(7)   Cisco-AVPair = "ip:inacl#2=deny ip any any"
On the switch the ACL is installed as xACSACLx-IP-WEB-ONLY-v1: the # characters become x. ISE does the same thing, but it adds a version string to the end of the name, so you will see something like xACSACLx-IP-WEB-ONLY-5f3a9b12. The switch then applies the ACL to the session, putting the client's IP address in place of any in the source field.
Lab Setup
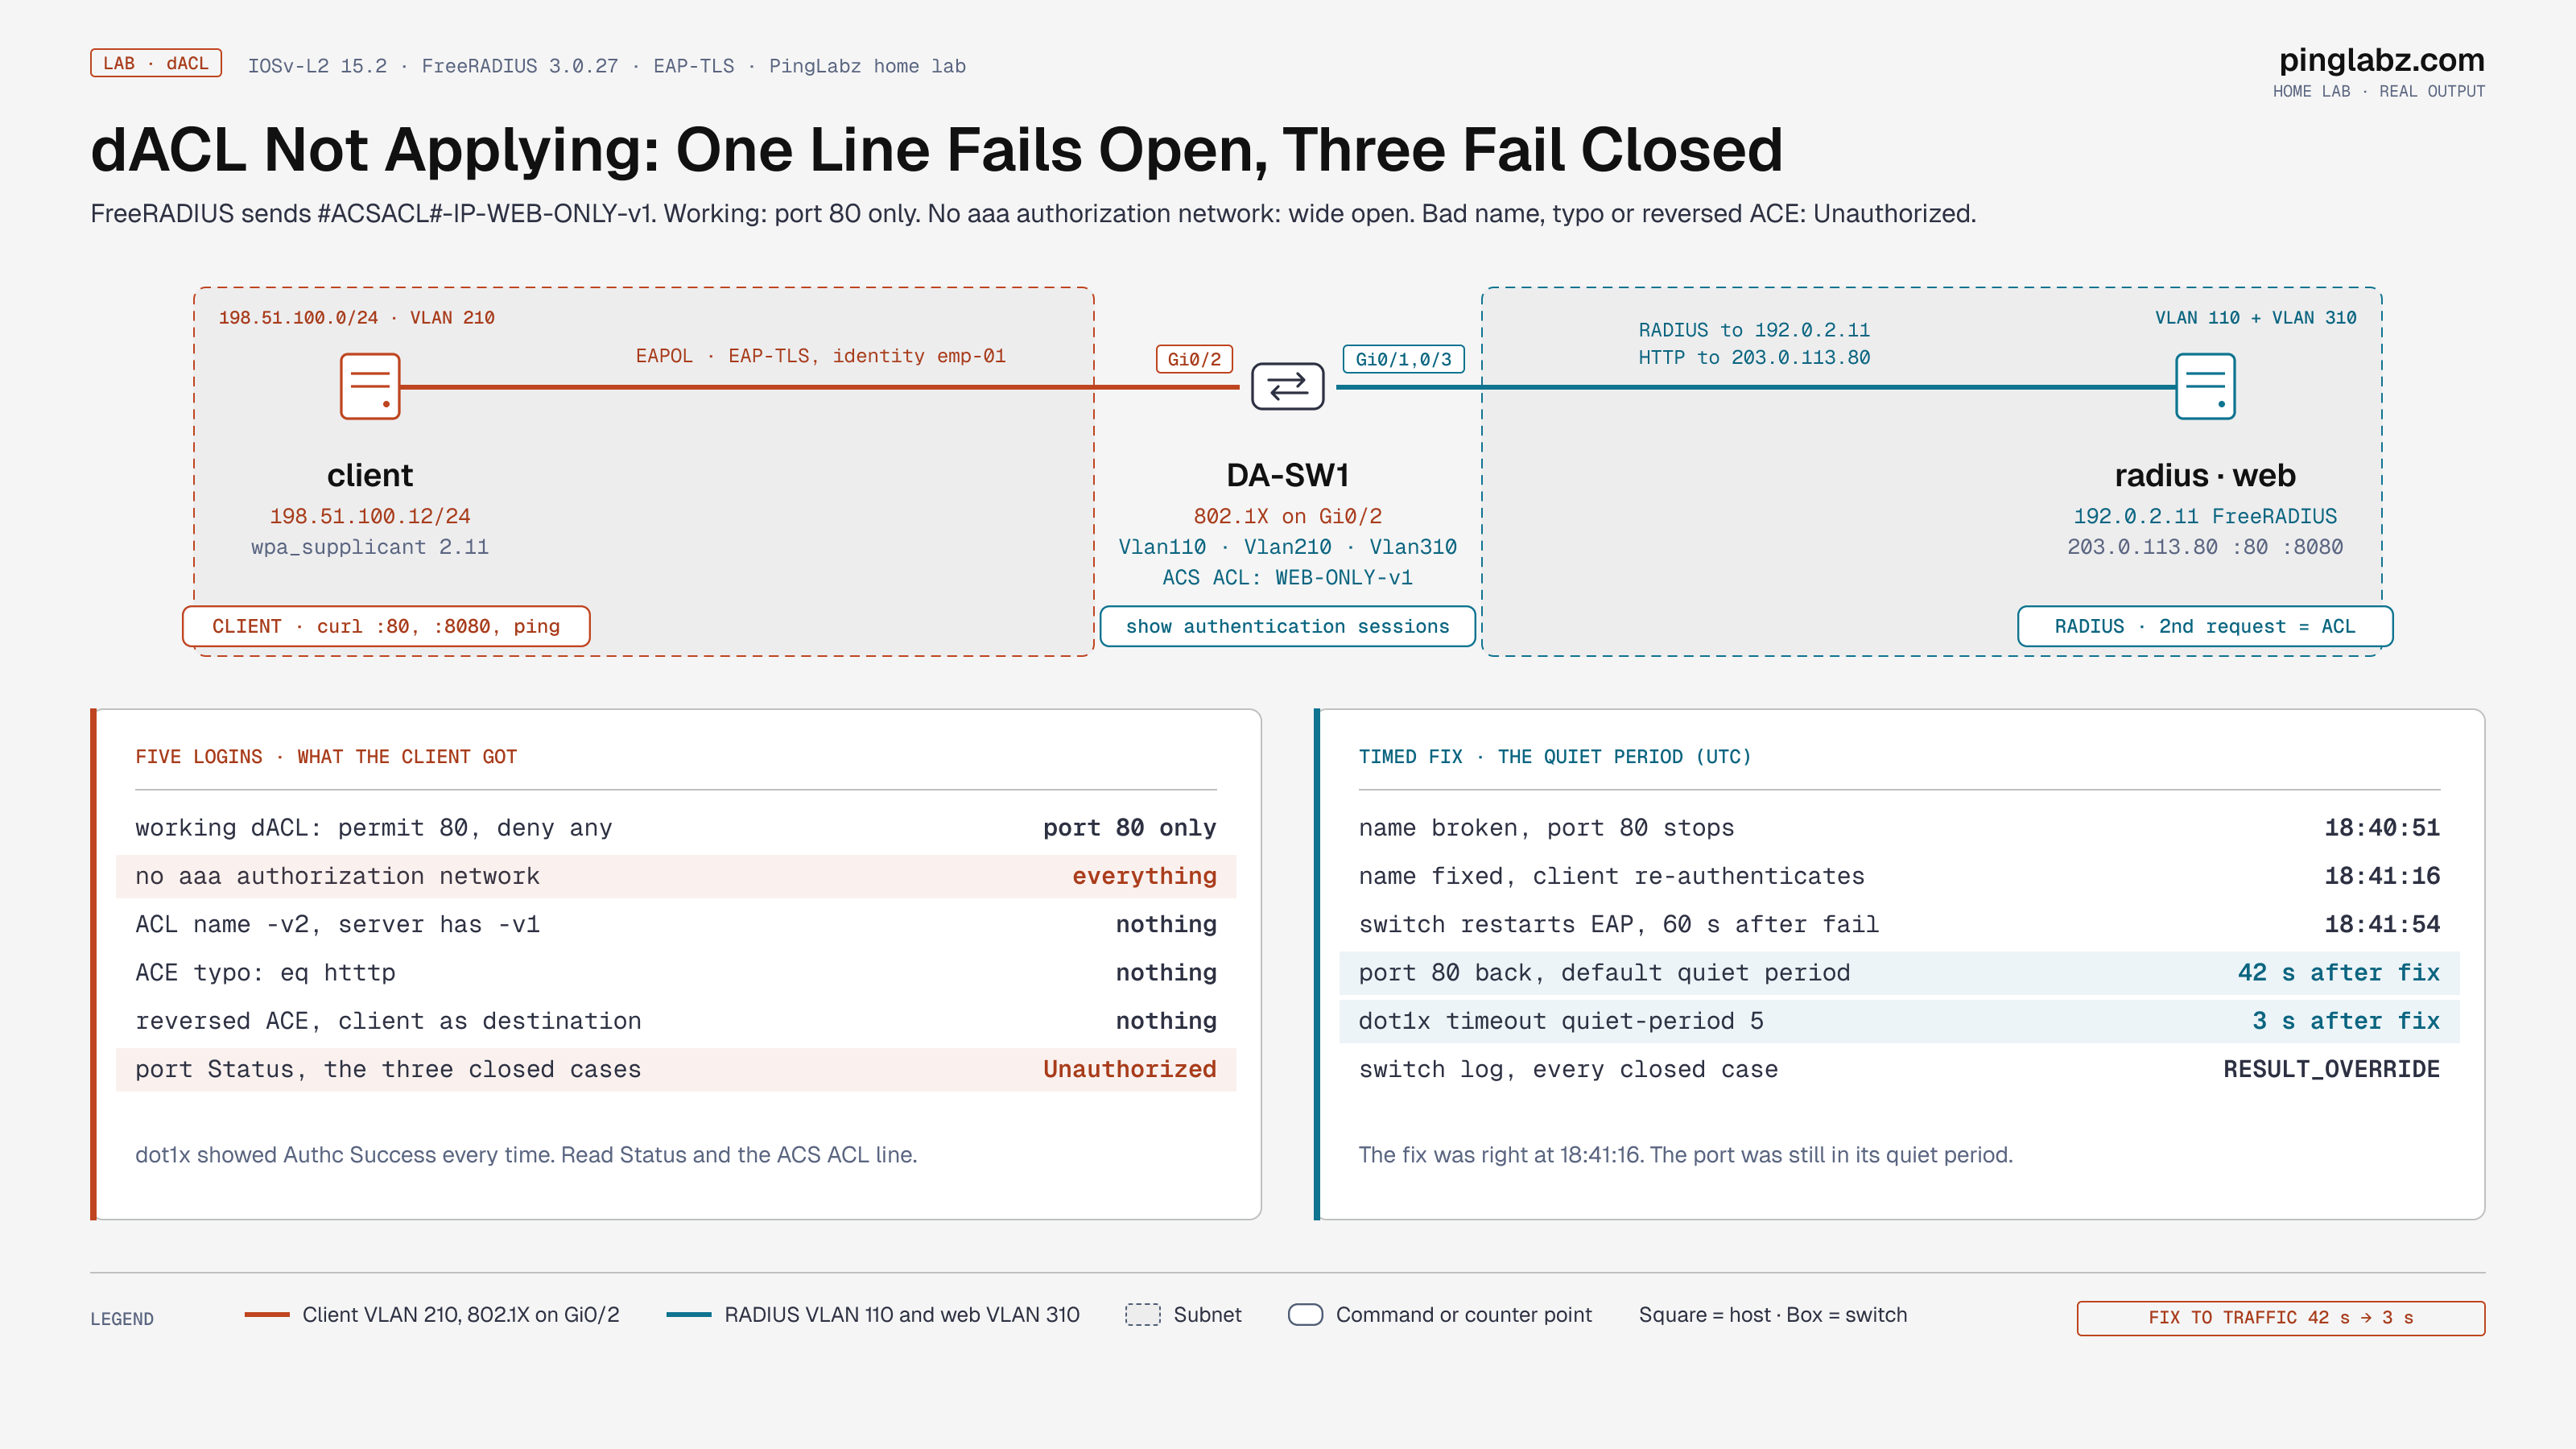
| Role | Address | Notes |
|---|---|---|
| DA-SW1 (IOSv-L2 15.2) | Vlan110 192.0.2.1, Vlan210 198.51.100.1, Vlan310 203.0.113.1 | Routes between the three VLANs |
| RADIUS (FreeRADIUS 3.0.27) | 192.0.2.11 on Gi0/1 | EAP-TLS, returns the dACL |
| Client (wpa_supplicant 2.11) | 198.51.100.12 on Gi0/2 | 802.1X port, identity emp-01 |
| Web server | 203.0.113.80 on Gi0/3 | HTTP on ports 80 and 8080 |
Before 802.1X was turned on, the client reached both web ports and could ping the server. The goal of the dACL is to allow port 80 and nothing else. The switch's 802.1X config:
aaa new-model
aaa authentication dot1x default group radius
aaa authorization network default group radius
!
radius server DACL-RADIUS
 address ipv4 192.0.2.11 auth-port 1812 acct-port 1813
 key <RADIUS_KEY>
ip radius source-interface Vlan110
radius-server vsa send authentication
dot1x system-auth-control
!
interface GigabitEthernet0/2
 switchport access vlan 210
 switchport mode access
 authentication host-mode single-host
 authentication port-control auto
 dot1x pae authenticator
 spanning-tree portfast edge
The FreeRADIUS users file. The first entry is the user and names the ACL. The second entry answers the download request:
emp-01
        Cisco-AVPair = "ACS:CiscoSecure-Defined-ACL=#ACSACL#-IP-WEB-ONLY-v1"

"#ACSACL#-IP-WEB-ONLY-v1" Auth-Type := Accept
        Cisco-AVPair = "ip:inacl#1=permit tcp any host 203.0.113.80 eq 80",
        Cisco-AVPair += "ip:inacl#2=deny ip any any"
On ISE the same result comes from an authorization profile with a DACL Name set, and the dACL body defined under Policy Elements, Results, Downloadable ACLs.
Step 1: Verify the dACL Is Being Applied
Here is the session after a good login, trimmed to the lines that matter:
DA-SW1#show authentication sessions interface GigabitEthernet0/2 details
            Interface:  GigabitEthernet0/2
          MAC Address:  aac1.ab70.84db
         IPv4 Address:  198.51.100.12
            User-Name:  emp-01
               Status:  Authorized
               Domain:  DATA
       Oper host mode:  single-host
       Current Policy:  POLICY_Gi0/2

Server Policies:
              ACS ACL:  xACSACLx-IP-WEB-ONLY-v1

Method status list:
      Method            State
      dot1x              Authc Success
How to read it: Status: Authorized means traffic is allowed through the port. ACS ACL under Server Policies means the switch downloaded the ACL and attached it to this session. IPv4 Address comes from IP Device Tracking, and the switch needs it to put the client's address into the ACL.
DA-SW1#show ip access-lists
Extended IP access list Auth-Default-ACL
    10 permit udp any any eq domain
    ...
    60 deny ip any any
Extended IP access list preauth_ipv4_acl (per-user)
    10 permit udp any any eq domain
    ...
    60 deny ip any any
Extended IP access list xACSACLx-IP-WEB-ONLY-v1 (per-user)
    1 permit tcp any host 203.0.113.80 eq www
    2 deny ip any any
(per-user) marks a downloaded ACL. The ACE numbers (1 and 2) are the inacl# numbers the server sent, not the 10, 20, 30 you get when you type an ACL by hand. IOS also shows port 80 as www.
DA-SW1#show ip device tracking all
Global IP Device Tracking for clients = Enabled
  IP Address    MAC Address   Vlan  Interface           Probe-Timeout      State    Source
198.51.100.12   aac1.ab70.84db 210  GigabitEthernet0/2     30              ACTIVE   ARP
On this 15.2 image, IP Device Tracking turned itself on for Gi0/2 once 802.1X was configured. On newer IOS XE the same job is done by device-tracking policies. If the IP address in the session is Unknown, look at tracking first.
Step 2: Prove It From the Client
Show commands tell you what the switch thinks. The client tells you what happens:
client:~$ curl -s -m 3 http://203.0.113.80/
PingLabz-80
client:~$ curl -s -m 3 http://203.0.113.80:8080/ || echo curl-8080-fail
curl-8080-fail
client:~$ ping -c 3 -W 1 203.0.113.80
3 packets transmitted, 0 packets received, 100% packet loss
Port 80 works. Port 8080 and ICMP hit deny ip any any. Before the client authenticated, all three failed. This switch image does not show hit counters on per-user ACEs, so a client-side test like this is the reliable check. On Catalyst hardware, show ip access-lists usually shows (N matches) next to each ACE.
permit udp any any eq domain and DHCP before the final deny, or it gets "authorized" and still cannot resolve a single name. ISE dACL blocks DNS walks through that exact failure.Step 3: Missing aaa authorization network (Fails Open)
I removed one line and logged in again:
DA-SW1(config)#no aaa authorization network default group radiusDA-SW1#show authentication sessions interface GigabitEthernet0/2 details | include Status|ACS ACL
Status: Authorized
DA-SW1#show ip access-lists | include per-user
Extended IP access list preauth_ipv4_acl (per-user)
client probe (port 80, port 8080, ping):
80:200 8080:200 ping:okThe Access-Accept still carried the dACL name. The RADIUS log shows the authentication exchange but no second request for #ACSACL#-IP-WEB-ONLY-v1. The switch never asked for the ACL. It authorized the port anyway, so the client had full access to everything. Nothing on the switch logged a warning.
That makes it the most dangerous fault in this article, because everything looks healthy. Status: Authorized and Authc Success are both true. The only sign is the missing ACS ACL line. Putting the line back and re-authenticating brought the dACL back: port 80 only.
Step 4: The ACL Name Does Not Match (Fails Closed)
Next, the user entry pointed at #ACSACL#-IP-WEB-ONLY-v2 while the server only had -v1. This is what happens when someone renames a dACL on ISE but the authorization profile still points at the old name, or the other way round.
(7)   User-Name = "#ACSACL#-IP-WEB-ONLY-v2"
(7)   Cisco-AVPair = "aaa:event=acl-download"
(7) ERROR: No Auth-Type found: rejecting the user via Post-Auth-Type = Reject
(7) Sent Access-Reject Id 16 from 192.0.2.11:1812 to 192.0.2.1:1645 length 38
DA-SW1#show authentication sessions interface GigabitEthernet0/2 details | include Status|dot1x
Status: Unauthorized
dot1x Authc Success
DA-SW1#show logging | include %
*Nov 14 18:38:30.996: %DOT1X-5-RESULT_OVERRIDE: Authentication result overridden for client (aac1.ab70.84db) on Interface Gi0/2 AuditSessionID C0000201000000130009CD77Read those together. EAP-TLS itself worked: the server sent an Access-Accept for emp-01. Only the download was rejected, so the switch overrode the result and left the port Unauthorized. No traffic passed at all, not even port 80. %DOT1X-5-RESULT_OVERRIDE is the message to search for when users say they authenticated but have no network.
Step 5: One Bad ACE Blocks the Whole Session
Two more faults, each on its own:
- A typo:
ip:inacl#1=permit tcp any host 203.0.113.80 eq htttp. - A reversed ACE:
ip:inacl#1=permit tcp host 203.0.113.80 eq 80 any, written as if the ACL filtered traffic towards the client.
In both cases the download itself succeeded. FreeRADIUS sent an Access-Accept with the ACEs. But the switch could not install the ACL, logged %DOT1X-5-RESULT_OVERRIDE again, and left the port Unauthorized with no per-user ACL. It did not install the good line and skip the bad one. The whole session failed.
The reversed ACE is the one people argue about. A dACL is an inbound ACL on the access port: the client is always the source. Write the client side as any and let the switch fill in the address. Put the server or subnet you are allowing in the destination field.
| Fault | Port status | Client traffic | Where it shows |
|---|---|---|---|
aaa authorization network missing | Authorized | Everything allowed | No ACS ACL line, no second RADIUS request |
| ACL name mismatch | Unauthorized | Nothing allowed | Access-Reject on the download, RESULT_OVERRIDE |
| ACE typo | Unauthorized | Nothing allowed | Download Accepted, RESULT_OVERRIDE |
| Reversed ACE (client as destination) | Unauthorized | Nothing allowed | Download Accepted, RESULT_OVERRIDE |
| Working dACL | Authorized | Port 80 only | ACS ACL: xACSACLx-IP-WEB-ONLY-v1 |
802.1X Troubleshooting: A Field Guide
Included with PingLabz Pro · 19 pages · US Letter PDF
Follow one connection through EAP, RADIUS, certificates, VLANs, dACLs, and CoA. Includes a published MAB case, exercises, and incident worksheets.
Already a member? Sign in.
Step 6: Why the Fix Took 42 Seconds to Work
To time a real outage, the client ran curl against port 80 about four times a second. I broke the ACL name, re-authenticated, fixed the name and re-authenticated again. These are the times from the client's probe log, in UTC:
| Time | Event |
|---|---|
| 18:40:51 | Name changed to -v2, client re-authenticates, port 80 stops answering |
| 18:40:54 | EAP starts, download rejected, port Unauthorized |
| 18:41:16 | Name fixed on the server, client logs off and on again |
| 18:41:54 | Switch finally restarts EAP, authentication succeeds |
| 18:41:58 | Port 80 answers again |
The fix was in place at 18:41:16, but nothing happened for 38 seconds. The switch started EAP again exactly 60 seconds after the failed attempt. That is the 802.1X quiet period. After a failure the port waits 60 seconds by default before it will authenticate that client again, and logging the client off and on does not cut the wait short.
Then I set a shorter quiet period on the port and ran the same test:
interface GigabitEthernet0/2
dot1x timeout quiet-period 5| Time | Event |
|---|---|
| 18:43:18 | Name broken, port 80 stops answering |
| 18:43:42 | Name fixed, client re-authenticates |
| 18:43:45 | EAP succeeds, port 80 answers again |
3 seconds from fix to traffic, against 42 with the default. When you are fixing a dACL during a change window, the quiet period is why the first retest seems to show your fix did not work. Wait it out before you change anything else. Shortening it on every port is a trade-off: a misconfigured client then retries every few seconds and fills your RADIUS logs.
Step 7: Editing a dACL That Is Already in Use
In the lab I changed the body of -v1 without renaming it (I added permit tcp any host 203.0.113.80 eq 8080), then re-authenticated. The switch downloaded the new body, and port 8080 opened:
DA-SW1#show ip access-lists xACSACLx-IP-WEB-ONLY-v1
Extended IP access list xACSACLx-IP-WEB-ONLY-v1 (per-user)
    1 permit tcp any host 203.0.113.80 eq www
    2 permit tcp any host 203.0.113.80 eq 8080
    3 deny ip any any
Only one session used this ACL, and it ended at logoff, so there was most likely no cached copy left to reuse. Sessions that stay up keep the old body until they re-authenticate. ISE solves the naming side by changing the version string in the name every time you save the dACL. The authorization profile does not change, but the switch sees a new name and downloads it. Existing sessions still need a re-authentication, which is what Change of Authorization is for. With FreeRADIUS or any server that does not version names for you, give each edit a new name (-v2) and change both entries together.
Step 8: Size and IPv6
Two limits I did not test here, but you should know about. Every ACE takes TCAM space for every session that uses it, so a 200-line dACL on a 48-port access switch can run out of hardware entries long before you expect. Keep dACLs short and summarise destinations. IPv6 needs its own ACEs (ipv6:inacl# on the wire). An IPv4-only dACL leaves IPv6 traffic to whatever the port's default policy allows, so check both when a dual-stack client gets through.
Gotchas
Authc Success is not the same as authorized. In every closed failure above, dot1x said Authc Success while the port was Unauthorized. Read the Status line.aaa authorization network before you open a case with the RADIUS team.AuditSessionID in RESULT_OVERRIDE matches the audit-session-id AVPair in the RADIUS request, and ISE Live Logs show the same value. Search by it.FAQ
Why does show authentication sessions not show an ACS ACL line?
Either the server did not send ACS:CiscoSecure-Defined-ACL, or the switch never downloaded it. In this lab, removing aaa authorization network default group radius left the client Authorized with no ACS ACL line and full network access.
What does %DOT1X-5-RESULT_OVERRIDE mean with a dACL?
Authentication passed but the switch could not apply the result. Here it appeared for a rejected download (name mismatch), an ACE typo and a reversed ACE. Each time the port stayed Unauthorized and passed no traffic.
Does a bad ACE in a dACL just get skipped?
No. One bad ACE stopped the whole ACL from installing, and the session was left Unauthorized.
Why does my dACL fix take a minute to work?
The 802.1X quiet period. After a failure the port waits 60 seconds by default. In this lab the fix took 42 seconds to reach the client with the default, and 3 seconds with dot1x timeout quiet-period 5.
Should the client be the source or the destination in a dACL ACE?
The source, written as any. The switch puts the client's IP address in its place. A reversed ACE with the client as the destination failed to install.
Scope: IOSv-L2 15.2 switch, single-host mode, IPv4, EAP-TLS. FreeRADIUS sent the same Cisco AVPairs ISE sends. On ISE, check the authorization profile's DACL Name and Live Logs for the download request. FreeRADIUS Filter-Id per-user ACLs covers the locally defined ACL alternative, which fails in a similar open/closed way.
Key Takeaways
- A dACL is two RADIUS exchanges. Look for the second Access-Request whose User-Name is
#ACSACL#-IP-.... - Missing
aaa authorization networkfails open: the port is Authorized with no ACL. - Name mismatches, typos and reversed ACEs fail closed:
Authc Success, thenRESULT_OVERRIDE, then an Unauthorized port. - After a failure, the 60-second quiet period delays your fix. It took 42 seconds here, against 3 seconds with a 5-second quiet period.
Next: troubleshooting 802.1X with show authentication sessions and debug, the full reference for every field used above. For the rest of the series, go back to the 802.1X guide.