

PEAP puts the user's password inside a TLS tunnel, and the only thing that decides who is on the other end of that tunnel is the client's check of the ISE server certificate. Get the check right and a fake RADIUS server gets nothing. Skip it and the client hands its MSCHAPv2 exchange to whoever answers first.
I tested all three cases in my home lab with Cisco ISE 3.5, a Cisco IOS access switch (15.2) and a Linux client running wpa_supplicant 2.11. With the ISE certificate trusted and the server name pinned, PEAP-MSCHAPv2 finished 0.99 to 1.02 seconds after EAPOL-Start. With the wrong CA on the client, the client rejected ISE 0.75 seconds in, before any password was sent, and ISE logged 5400 Authentication failed, 12321 PEAP failed SSL/TLS handshake because the client rejected the ISE local-certificate. The client then waited 60 seconds before it tried again. With no CA configured at all, the login succeeded, which is the dangerous result.
How PEAP authenticates the server
PEAP runs in two phases. In phase 1 ISE sends its EAP certificate and the client builds a TLS tunnel to it. In phase 2 the client proves the user's password with EAP-MSCHAPv2 inside that tunnel. The switch only relays EAP between EAPOL and RADIUS and never sees inside the tunnel, so nothing about PEAP is configured on the switch.
The client should check two things about the certificate in phase 1:
- Who signed it. The issuing CA, or the certificate itself if it is self-signed, has to be in the client's trusted list for this network. In wpa_supplicant that is
ca_cert. In Windows it is the "Trusted Root Certification Authorities" list in the PEAP settings. - Which server it names. The certificate's DNS name has to match the server you expect. In wpa_supplicant that is
domain_match. In Windows it is "Connect to these servers".
Without both, any certificate from any public CA, or a self-signed one with the right name, would satisfy the client.
The lab
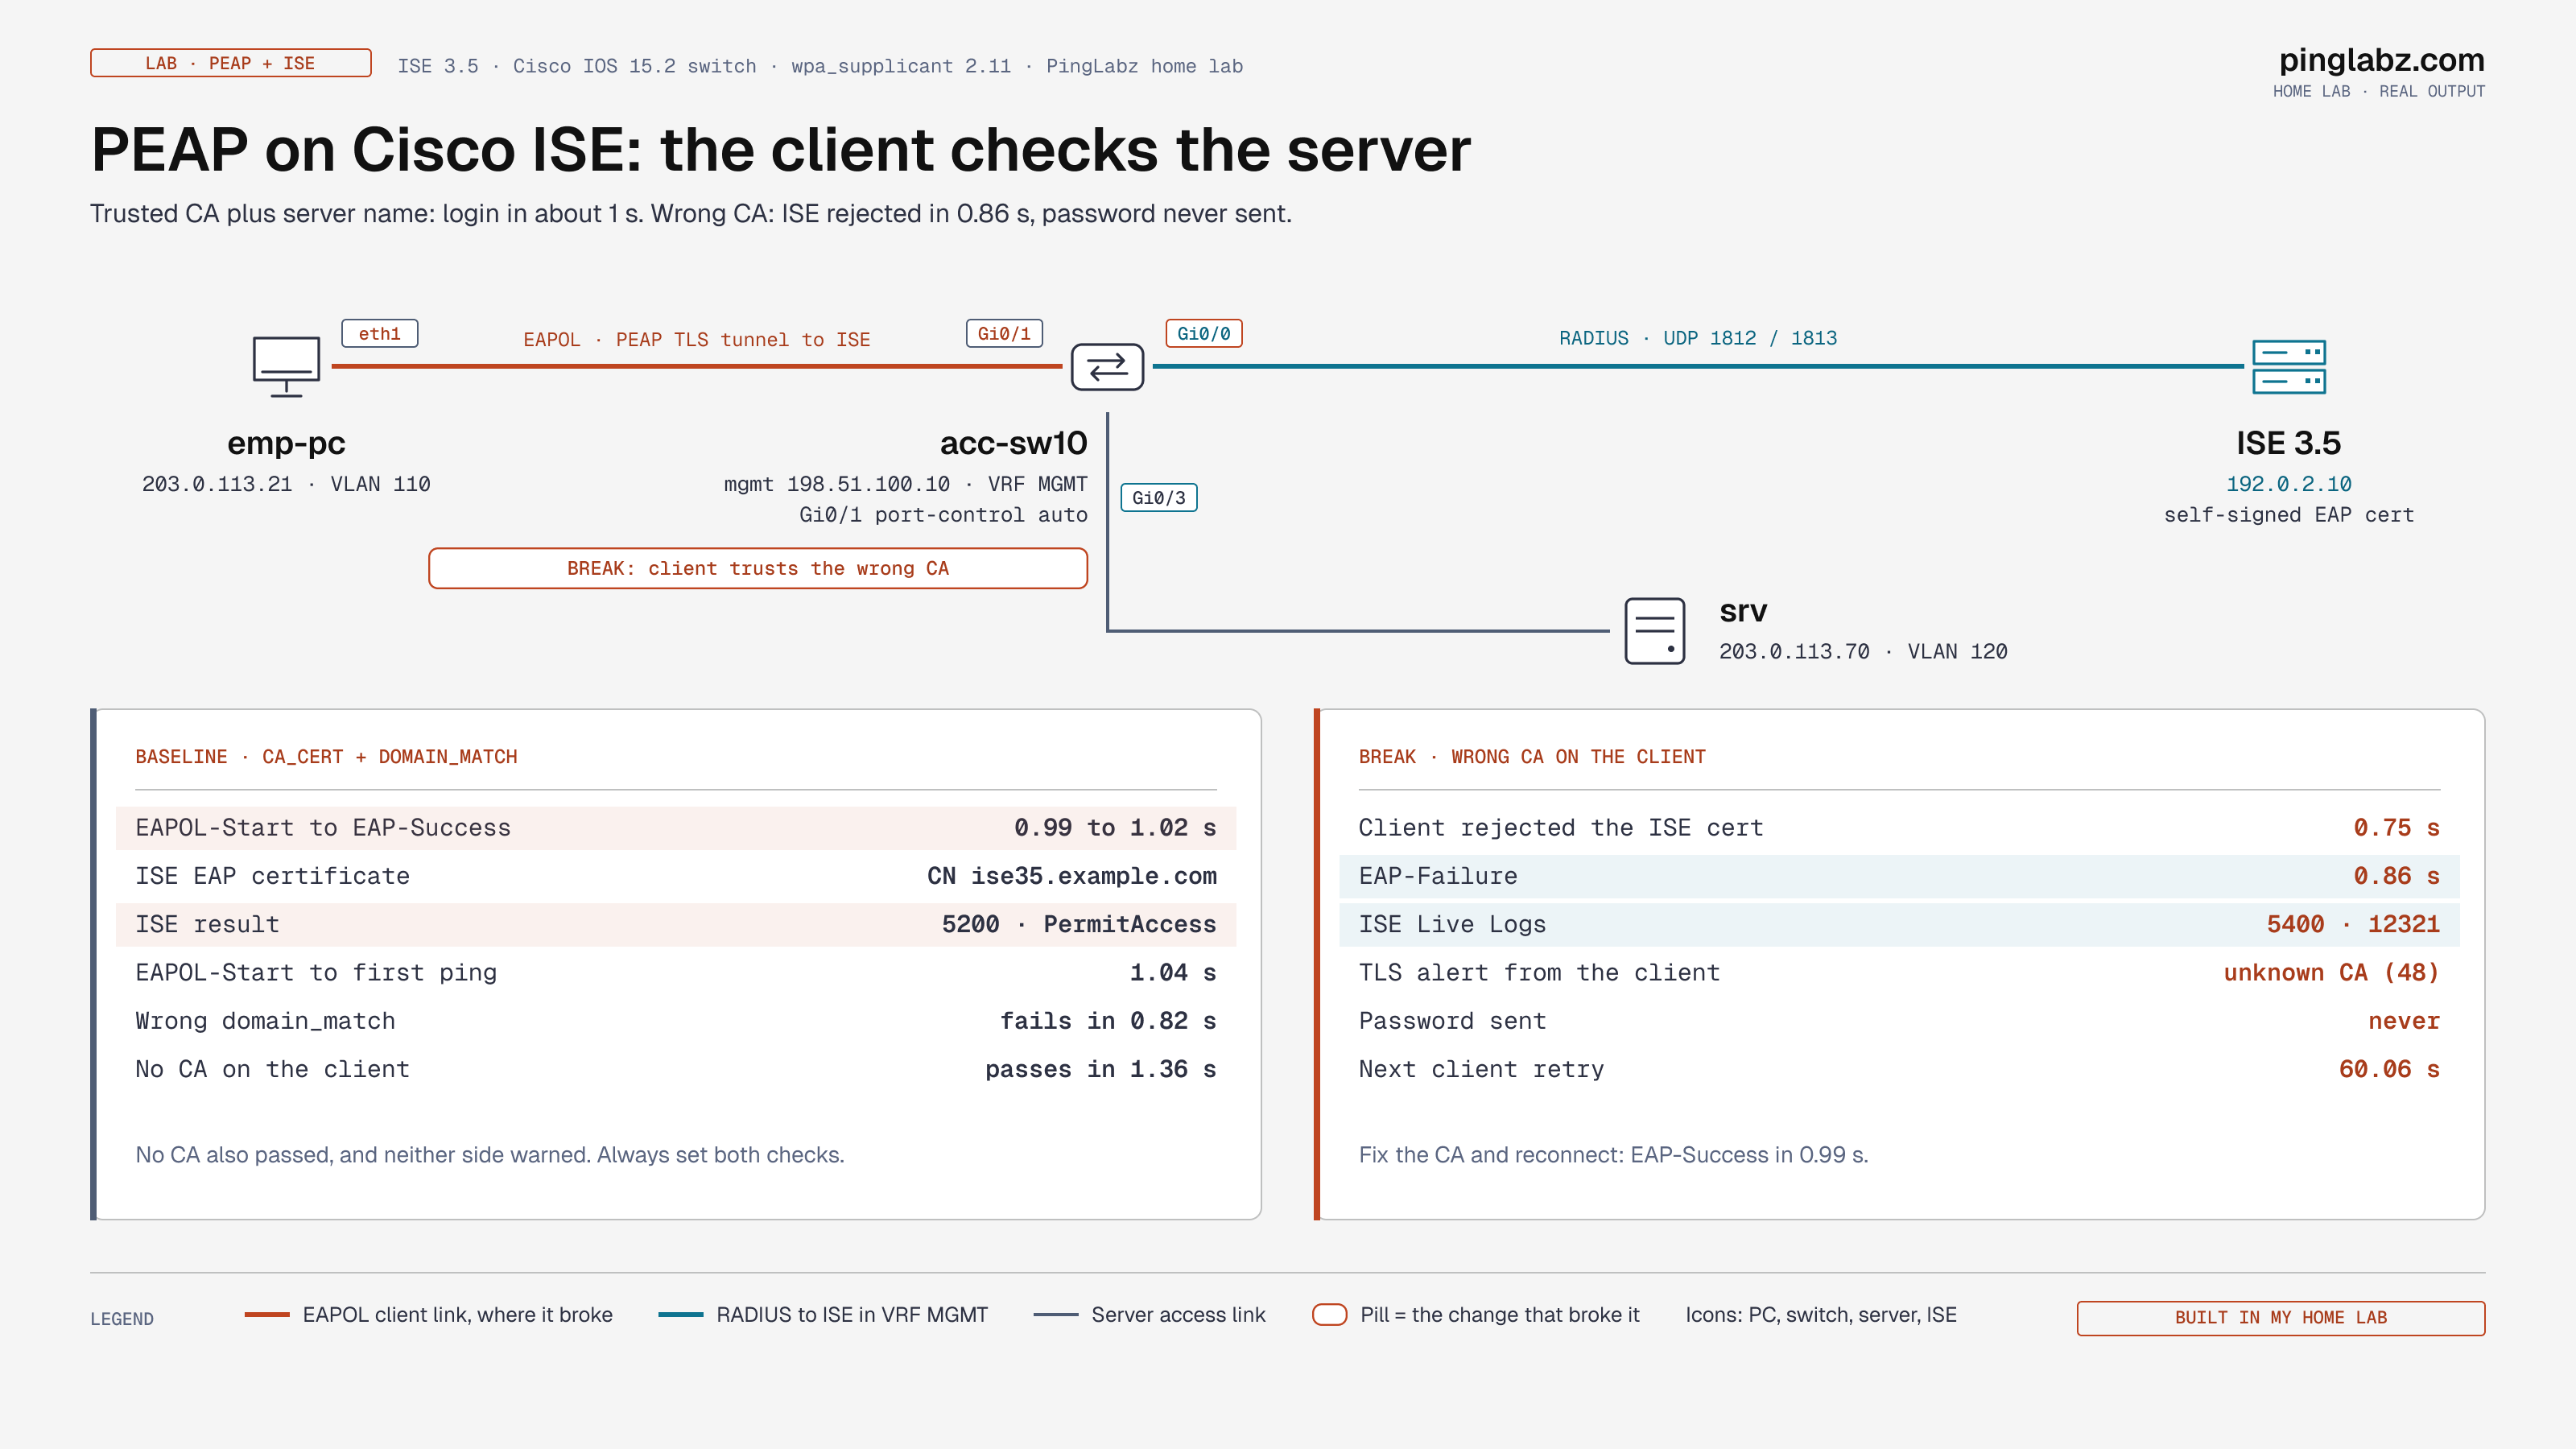
| Device | Addressing | Role |
|---|---|---|
| ISE 3.5 (standalone) | 192.0.2.10 | RADIUS server. EAP certificate CN ise35.example.com. Policy set DD-Wired, internal user emp-01 in group DD-Staff |
| acc-sw10, Cisco IOS access switch (15.2) | Gi0/0 198.51.100.10 in VRF MGMT | Authenticator. Same 802.1X and RADIUS configuration as the wired 802.1X guide |
| emp-pc, Linux | 203.0.113.21 on Gi0/1, VLAN 110 | Supplicant: wpa_supplicant 2.11, PEAP-MSCHAPv2 |
| srv, Linux | 203.0.113.70 on Gi0/3, VLAN 120 | Ping target, every 100 ms, to show when the port opens |
The switch, network device and policy set are the ones built in the wired 802.1X configuration guide. The only thing that changes between the tests below is the client's configuration file.
Step 1: Check which certificate ISE uses for EAP
Administration > System > Certificates > System Certificates. Find the row whose Used By column includes EAP Authentication. That certificate is what every PEAP and EAP-TLS client will see. Note its Issued By and its name, because those two values go into the client.
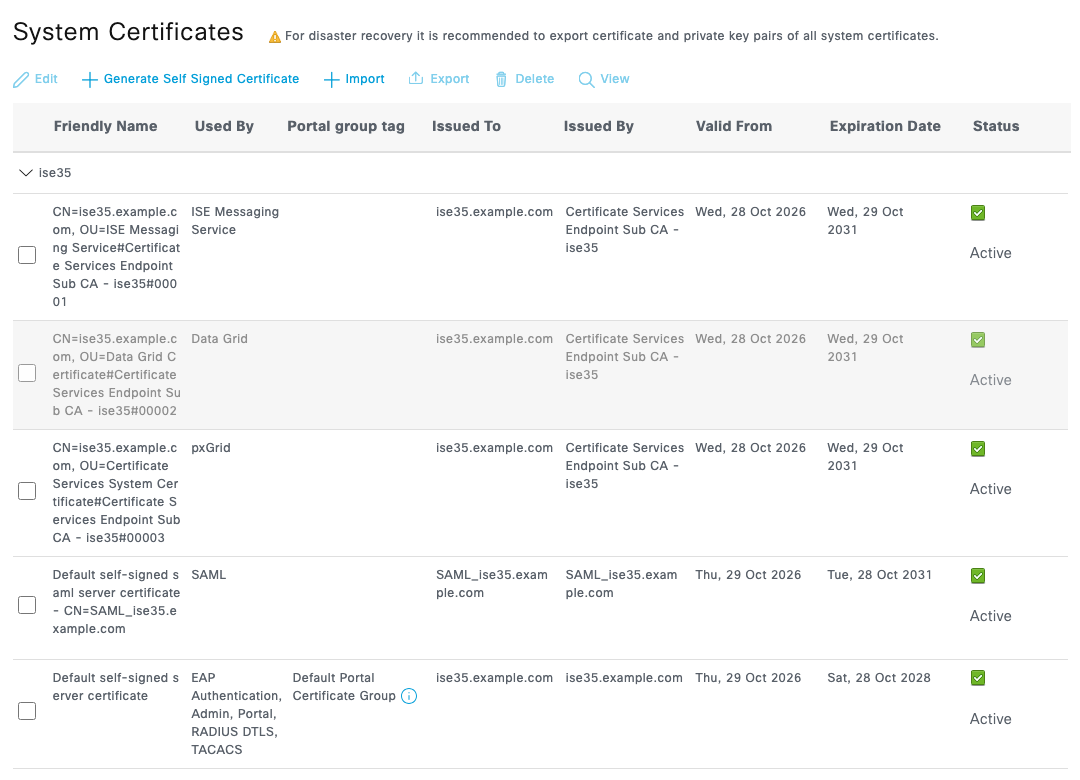
A lab can live with the self-signed default. In production, replace it with a certificate from your internal CA and give the clients that CA, so a renewed ISE certificate does not break every client. The certificate name should be a DNS name the clients can pin, such as ise.example.com. ISE allows PEAP in the Default Network Access allowed protocols, so no protocol change is needed. If you build your own allowed-protocols list, tick PEAP and EAP-MSCHAPv2 under it.
To get the certificate onto a test client, export the public certificate only (System Certificates > select the row > Export > Export Certificate Only). Never export the private key for this.
Step 2: Configure the client to check the server
This is the working client file. ca_cert is the exported ISE certificate and domain_match pins the name in it.
ctrl_interface=/var/run/wpa_supplicant
ap_scan=0
network={
  key_mgmt=IEEE8021X
  eap=PEAP
  identity="emp-01"
  password="<USER_PASSWORD>"
  ca_cert="/etc/wpa/ise-ca.pem"
  domain_match="ise35.example.com"
  phase2="auth=MSCHAPV2"
  eapol_flags=0
}
The client log shows both checks passing before the inner method starts:
EAPOL: txStart
CTRL-EVENT-EAP-PROPOSED-METHOD vendor=0 method=13 -> NAK
CTRL-EVENT-EAP-METHOD EAP vendor 0 method 25 (PEAP) selected
CTRL-EVENT-EAP-PEER-CERT depth=0 subject='/CN=ise35.example.com'
CTRL-EVENT-EAP-PEER-ALT depth=0 DNS:ise35.example.com
TLS: Match domain against ise35.example.com
EAP: Status notification: remote certificate verification (param=success)
CTRL-EVENT-EAP-SUCCESS EAP authentication completed successfully
On Windows, the same two settings are in the network adapter's Authentication tab under PEAP settings: tick "Verify the server's identity by validating the certificate", fill "Connect to these servers" with the ISE name, and tick only your CA in the trusted list. Enabling 802.1X on Windows 11 walks through the screens. For a domain, push the same values with a Wired Network Policy in Group Policy so users never see a trust prompt.
Results: four client configurations
Each run started a fresh supplicant on emp-pc with the ping already running, after clearing the session on Gi0/1. Times are from the client's EAPOL-Start.
| Client configuration | Result | Time | What ISE logged |
|---|---|---|---|
| Correct CA + domain_match | EAP-Success, port authorized | 0.99 to 1.02 s, first ping 1.04 s | 5200 Authentication succeeded |
| Wrong CA (Other Corp Root CA) | Client rejects ISE, TLS alert unknown CA | EAP-Failure at 0.86 s, retry after 60.06 s | 5400, 12321 client rejected the ISE local-certificate |
| Correct CA, wrong domain_match | Client rejects ISE, Domain mismatch | EAP-Failure at 0.82 s | No new row (see below) |
| No CA at all | EAP-Success, port authorized | 1.36 s | 5200 Authentication succeeded |
The last row is the one to remember. With no ca_cert, wpa_supplicant reported "remote certificate verification (param=success)" for a certificate it had no way to check. ISE also showed a normal pass. Nothing on either side warns you that this client would have run MSCHAPv2 with any server that answered.
Failure and fix: the client trusts the wrong CA
To break it I pointed ca_cert at a different self-signed CA, CN=Other Corp Root CA. This is what happens when a client is built with the old ISE certificate, the wrong internal CA, or a public CA list that does not include yours.
EAPOL: txStart
CTRL-EVENT-EAP-METHOD EAP vendor 0 method 25 (PEAP) selected
CTRL-EVENT-EAP-PEER-CERT depth=0 subject='/CN=ise35.example.com'
TLS: Certificate verification failed, error 18 (self-signed certificate) depth 0 for '/CN=ise35.example.com'
CTRL-EVENT-EAP-TLS-CERT-ERROR reason=1 depth=0 subject='/CN=ise35.example.com' err='self-signed certificate'
EAP: Status notification: local TLS alert (param=unknown CA)
CTRL-EVENT-EAP-FAILURE EAP authentication failed
   ... 60 s later ...
EAPOL: txStart
The client received ISE's certificate 0.75 seconds after EAPOL-Start, could not chain it to the CA it was given, and sent a TLS alert. EAP-Failure followed at 0.86 seconds. The password never left the client, because the failure happened in phase 1. Over 75 seconds the client sent two EAPOL-Starts, failed both, and got 0 ping replies.
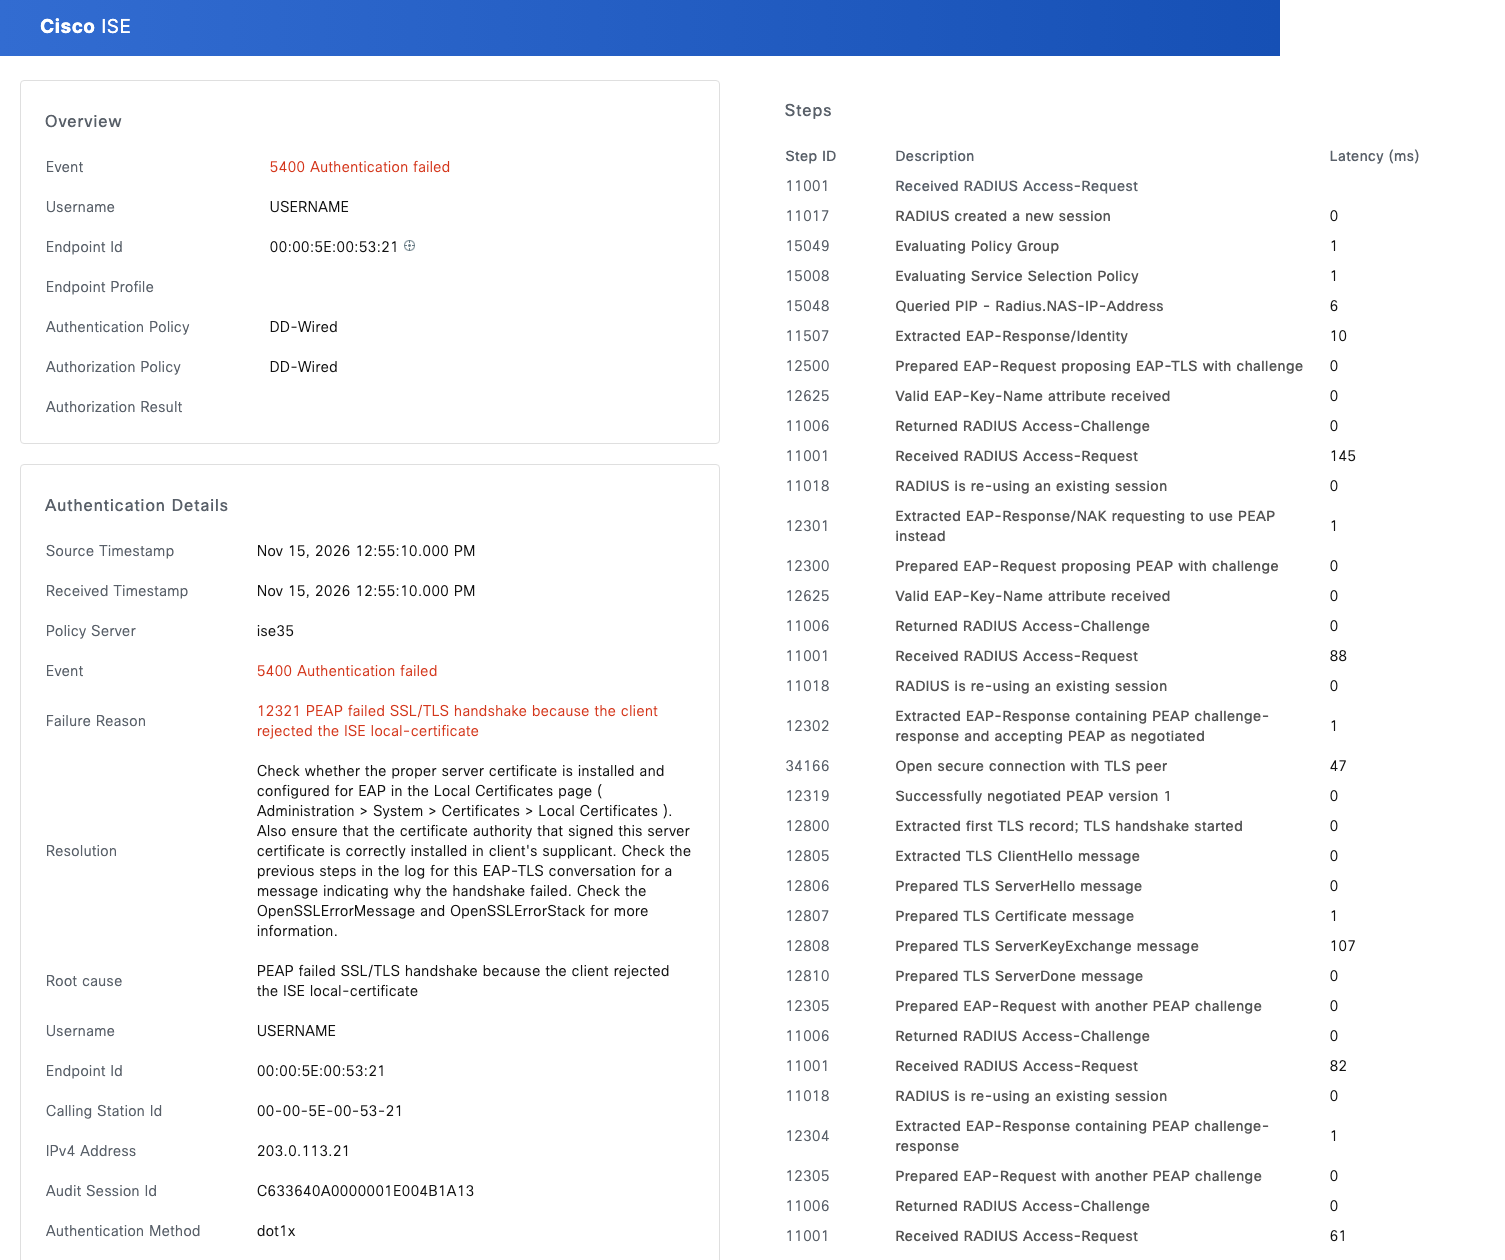
ISE gets enough of the conversation to say exactly what went wrong. The steps list shows ISE sending its certificate (12807), then receiving the client's alert (12815), then 12321. The OpenSSL error attribute in the same report reads tlsv1 alert unknown ca ... SSL alert number 48, which is the client telling ISE it does not know the CA. The whole exchange took 5 Access-Challenges and one Access-Reject, with a response time of 191 ms.
The fix is on the client, not ISE. I put the correct certificate back in ca_cert and restarted the supplicant. EAP-Success came 0.99 seconds after EAPOL-Start and the first ping 1.04 seconds after it. Without the restart, the client would have tried again on its own only after its 60-second wait, so on a real desk the fastest recovery is to fix the profile and reconnect.
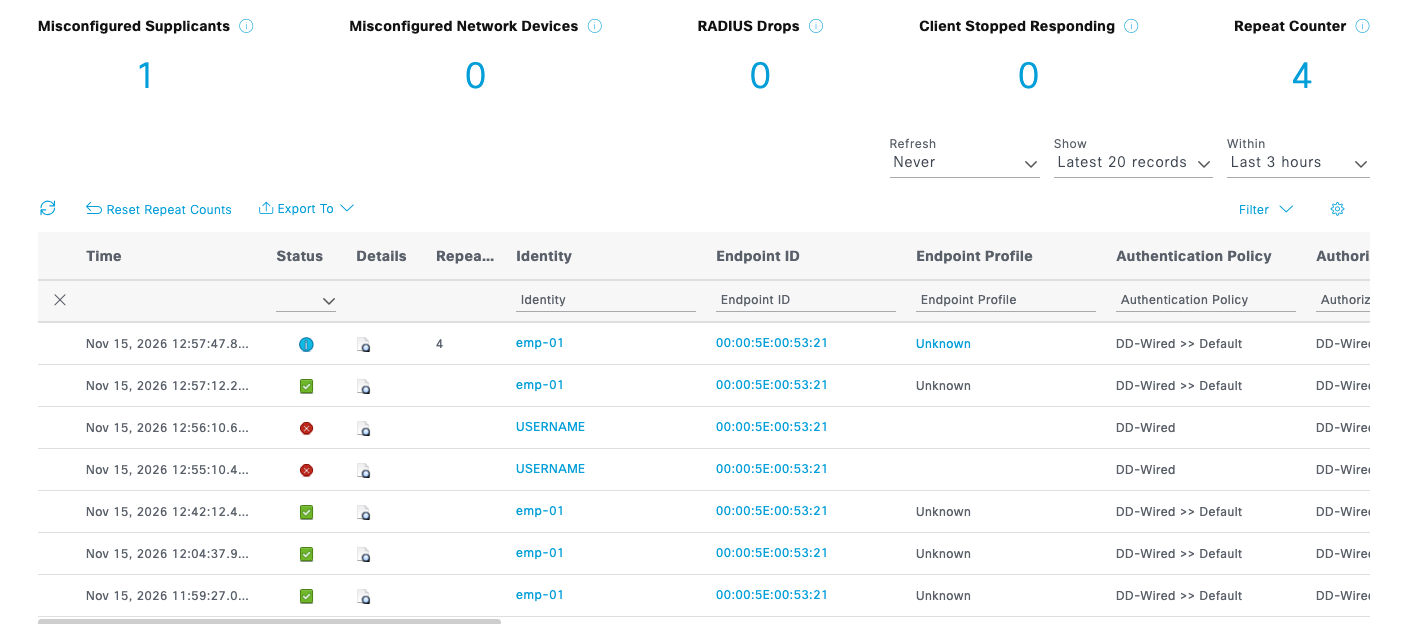
The name check fails quietly in Live Logs
The domain mismatch test is worth a separate note. The client had the right CA but expected radius.example.com. It failed 0.82 seconds after EAPOL-Start with "Domain mismatch" and a TLS internal error alert. ISE handled the conversation, but Live Logs showed no new row for it, only the Misconfigured Supplicants counter at 1. The earlier wrong-CA failures from the same endpoint had already been logged, and ISE suppresses repeated failures from a client it has flagged as misconfigured. The suppression settings are under Administration > System > Settings > Protocols > RADIUS.
So if a user says it still fails after you changed something, and Live Logs shows nothing new, do not assume the request stopped reaching ISE. Check the counters at the top of Live Logs and the client's own log before you look at the switch.
Gotchas
Other PEAP failures, such as a wrong password or an unknown user, happen in phase 2 and do reach the identity store. The ISE Live Logs failure-code casebook reproduces those.
FAQ
Does PEAP need any switch configuration?
No. The switch only relays EAP. The same aaa authentication dot1x, RADIUS server and dot1x pae authenticator lines carry PEAP, EAP-TLS or any other EAP method. The lab used the configuration from the wired 802.1X guide without a change.
What does ISE 12321 mean?
"PEAP failed SSL/TLS handshake because the client rejected the ISE local-certificate." ISE sent its EAP certificate and the client sent a TLS alert back. In this lab the alert was unknown CA (alert number 48). Fix the trusted CA or the server name on the client.
Is my password exposed when the server certificate check fails?
Not when the check is on. The client rejected ISE in phase 1, 0.75 seconds after EAPOL-Start, before any MSCHAPv2 exchange. With no CA configured, the client finishes the login with whatever server answers, which is how rogue RADIUS servers collect MSCHAPv2 exchanges.
Should I use the ISE self-signed certificate for PEAP?
Only in a lab. Every client has to trust that one certificate, and it changes when you regenerate it. Use a certificate from your internal CA and give clients the CA plus the server name.
How long does a PEAP login take with ISE?
About one second here. 0.99 to 1.02 seconds from EAPOL-Start to EAP-Success with the certificate and name checks on, and 1.36 seconds in the run without a CA.
Not covered here: Active Directory as the identity source and machine authentication. The PEAP exchange is the same. Only the identity store in the authentication rule changes.
Key takeaways
- PEAP security comes from the client checking the ISE certificate and name. Set both
ca_certanddomain_match, or the trusted CA and "Connect to these servers" on Windows. - A wrong CA fails in 0.86 seconds with ISE 12321 and no credential sent. The fix is on the client.
- A client with no CA logs in normally, and neither side warns you.
- Repeated failures from the same client can stop showing in Live Logs. Read the counters and the client log.
802.1X Troubleshooting: A Field Guide
Included with PingLabz Pro · 19 pages · US Letter PDF
Follow one connection through EAP, RADIUS, certificates, VLANs, dACLs, and CoA. Includes a published MAB case, exercises, and incident worksheets.
Already a member? Sign in.
Next in the wired 802.1X deep dive: EAP-TLS certificates on Cisco ISE and IOS XE, where the client proves itself with a certificate too. Before this: wired 802.1X with ISE end to end. Related: EAPOL explained and 802.1X troubleshooting with show authentication sessions. All the ISE labs are in the Cisco ISE lab series.