
VLAN hopping is a class of Layer 2 attacks that lets a malicious host on one VLAN reach another VLAN without going through a router or firewall. It bypasses every Layer 3 control you have. Most networks are still vulnerable to it because the defaults that enable it (Dynamic Trunking Protocol on every port, native VLAN of 1) are still defaults.
This article walks through the two main VLAN hopping attacks, how they actually work at the protocol level, the four-line configuration that defeats both, and the broader Layer 2 hardening pattern. If you are a network or security engineer responsible for a Cisco-based campus, treat this as the minimum-required read.
The Threat Model
VLAN hopping assumes the attacker is on the network. They are connected to a switch port (perhaps a wall jack in a conference room, perhaps a VM in a virtualized fabric) on one VLAN. From there, they want to reach a different VLAN: the server VLAN, the management VLAN, the voice VLAN.
The conventional defense is that VLANs are isolated at Layer 2. The only way out is through a Layer 3 gateway, where you presumably have ACLs and inspection. VLAN hopping defeats this assumption. The attacker reaches the target VLAN at Layer 2, before any router gets a chance to apply policy.
Two attacks dominate: switch spoofing (DTP-based) and double tagging (native VLAN-based).
Attack #1: Switch Spoofing via DTP
Cisco's Dynamic Trunking Protocol (DTP) is enabled by default on Catalyst switch ports. Its purpose is automatic trunk negotiation: if you connect two switches, DTP detects this and forms a trunk without manual configuration. The default mode is dynamic auto, which will form a trunk if the other side initiates.
The attack: the malicious host on the access port speaks DTP and proposes "I am a switch, let's negotiate a trunk." The Catalyst switch agrees (default behavior of dynamic auto when receiving a desirable proposal), and the port becomes a trunk. Now the attacker receives every VLAN that is allowed on the trunk, which by default is every VLAN that exists on the switch.
The walk-through:
- Attacker plugs into a wall jack. Default Cisco port config:
switchport mode dynamic auto, native VLAN 1. - Attacker runs a tool like Yersinia that crafts DTP packets advertising
desirablemode. - Switch sees the DTP advertisement, transitions the port to trunk mode automatically.
- Attacker now sees 802.1Q-tagged frames for every VLAN configured on the switch. Connecting to any VLAN is a matter of joining a virtual interface to that VLAN ID and getting an IP via DHCP for that subnet.
The attacker can now ARP, DHCP, send any frame, and receive any frame on any VLAN. From the network's perspective, the attacker is just another switch.
Defense: Disable DTP Everywhere
The fix is two lines per access port:
Switch(config-if)# switchport mode access
Switch(config-if)# switchport nonegotiate
The first command pins the port to access mode. The second disables DTP entirely (sends no DTP frames, ignores received DTP frames). With both in place, the port cannot become a trunk via negotiation. An attacker speaking DTP gets no response.
For trunk ports between switches:
Switch(config-if)# switchport mode trunk
Switch(config-if)# switchport trunk encapsulation dot1q
Switch(config-if)# switchport nonegotiate
The trunk is configured manually (no DTP). This is the PingLabz default for every trunk in production.
Keep the port mode explicit and verify negotiation on the image you use. In the IOL-L2 17.18.2 lab below, a static access port already reported Negotiation of Trunking: Off without an explicit switchport nonegotiate line in its running configuration. The static trunk reported negotiation On until switchport nonegotiate was applied. Use show interfaces switchport to check the operational state rather than assuming every static access port still sends DTP.
Attack #2: Double Tagging via the Native VLAN
Native VLAN frames cross trunks untagged. An attacker on the native VLAN can craft a frame with two 802.1Q tags: an outer tag matching the native VLAN, and an inner tag matching the target VLAN. When the frame hits the first switch, the switch strips the outer tag (because it matches the native VLAN, which is sent untagged across the trunk), and then forwards the frame across the trunk with only the inner tag intact. The next switch sees a frame tagged for the target VLAN and forwards it accordingly.
The walk-through:
- The attacker on an access port in VLAN 1 sends a frame with two 802.1Q tags: outer VID 1, matching the trunk's native VLAN, and inner VID 100, the target VLAN.
- On a switch that accepts this tagged ingress, the first switch classifies the frame into VLAN 1 using the outer tag. The inner tag remains inside the frame.
- When the first switch forwards the frame onto a trunk whose native VLAN is 1, it removes the outer VLAN 1 tag. The inner VLAN 100 tag is now the only tag on the wire.
- The trunk peer reads VID 100 and forwards the frame into VLAN 100. The lab below captures this sequence with outer VLAN 10 and inner VLAN 20.
This attack is one-way: the attacker can send into the target VLAN, but cannot receive responses (because the response would be tagged VID 100 over the trunk, which the first switch would direct to VLAN 100, not VLAN 1 where the attacker actually is). For attacks like sending DHCP starvation, ARP spoofing, or single-direction packet injection (some exploits), one-way is enough.
Defense: Move the Native VLAN, Tag It Explicitly
Two complementary mitigations:
1. Change the native VLAN away from VLAN 1 on every trunk.
Switch(config)# vlan 999
Switch(config-vlan)#  name UNUSED-NATIVE
Switch(config-vlan)# exit

Switch(config)# interface range GigabitEthernet1/0/24-26
Switch(config-if-range)#  switchport trunk native vlan 999
Now an attacker in VLAN 1 cannot use the double-tag trick because VLAN 1 is no longer the native VLAN. VLAN 999 is, and you have ensured no host port is in VLAN 999.
2. Force the native VLAN to be tagged on the trunk.
Switch(config)# vlan dot1q tag nativeThis global command tells the switch to add an explicit 802.1Q tag for the native VLAN frames as well, instead of sending them untagged. Now there is no untagged-native shortcut for the attack to exploit. Every frame on the trunk has a tag, and a doubly-tagged attacker frame appears as such.
Either mitigation alone is effective; both together is defense in depth.
Worth knowing that the untagged-native shortcut shows up by accident far more often than it shows up in an attack. A native VLAN mismatch between two trunk neighbors merges two VLANs into one without anybody crafting a frame, which is the same primitive double tagging abuses deliberately, so learning to spot it in the CDP logs pays off twice.
This Is Not a Cisco-Only Issue
VLAN hopping works on any 802.1Q-compliant switch from any vendor that allows untagged native VLAN frames on trunks. The DTP variant is Cisco-specific (DTP is Cisco-proprietary), but the double-tagging variant is universal. Juniper, Arista, HP/Aruba switches all share the same native-VLAN behavior by default and require equivalent mitigations.
The Broader Layer 2 Hardening Checklist
VLAN hopping is one of about a dozen Layer 2 attacks. Here is the production hardening pattern in the order we recommend applying it:
switchport nonegotiatevlan dot1q tag nativeThe full configuration patterns for each are in VLAN Security Hardening: Protecting Your Layer 2 Network.
Containerlab Lab: Double Tagging on the Wire
Three crafted frames entered SW1 through an access port in VLAN 10. All three reached B's access port in VLAN 20. After changing the trunk's native VLAN to an unused VLAN 99, the same three frames stayed double-tagged on the trunk and none reached B.
This test ran on two Cisco IOL-L2 switches running IOS 17.18.2, with Linux hosts in Containerlab. IOL-L2 reproduced the attack; IOSv-L2 was not deployed or tested. The result applies to this image and configuration. Tagged ingress on an access port is a behavior to verify on your platform.
Topology and Soft-Trunk Baseline
A connects to SW1, SW1 trunks to SW2, and SW2 connects to B. There is no routed path between the two user VLANs.
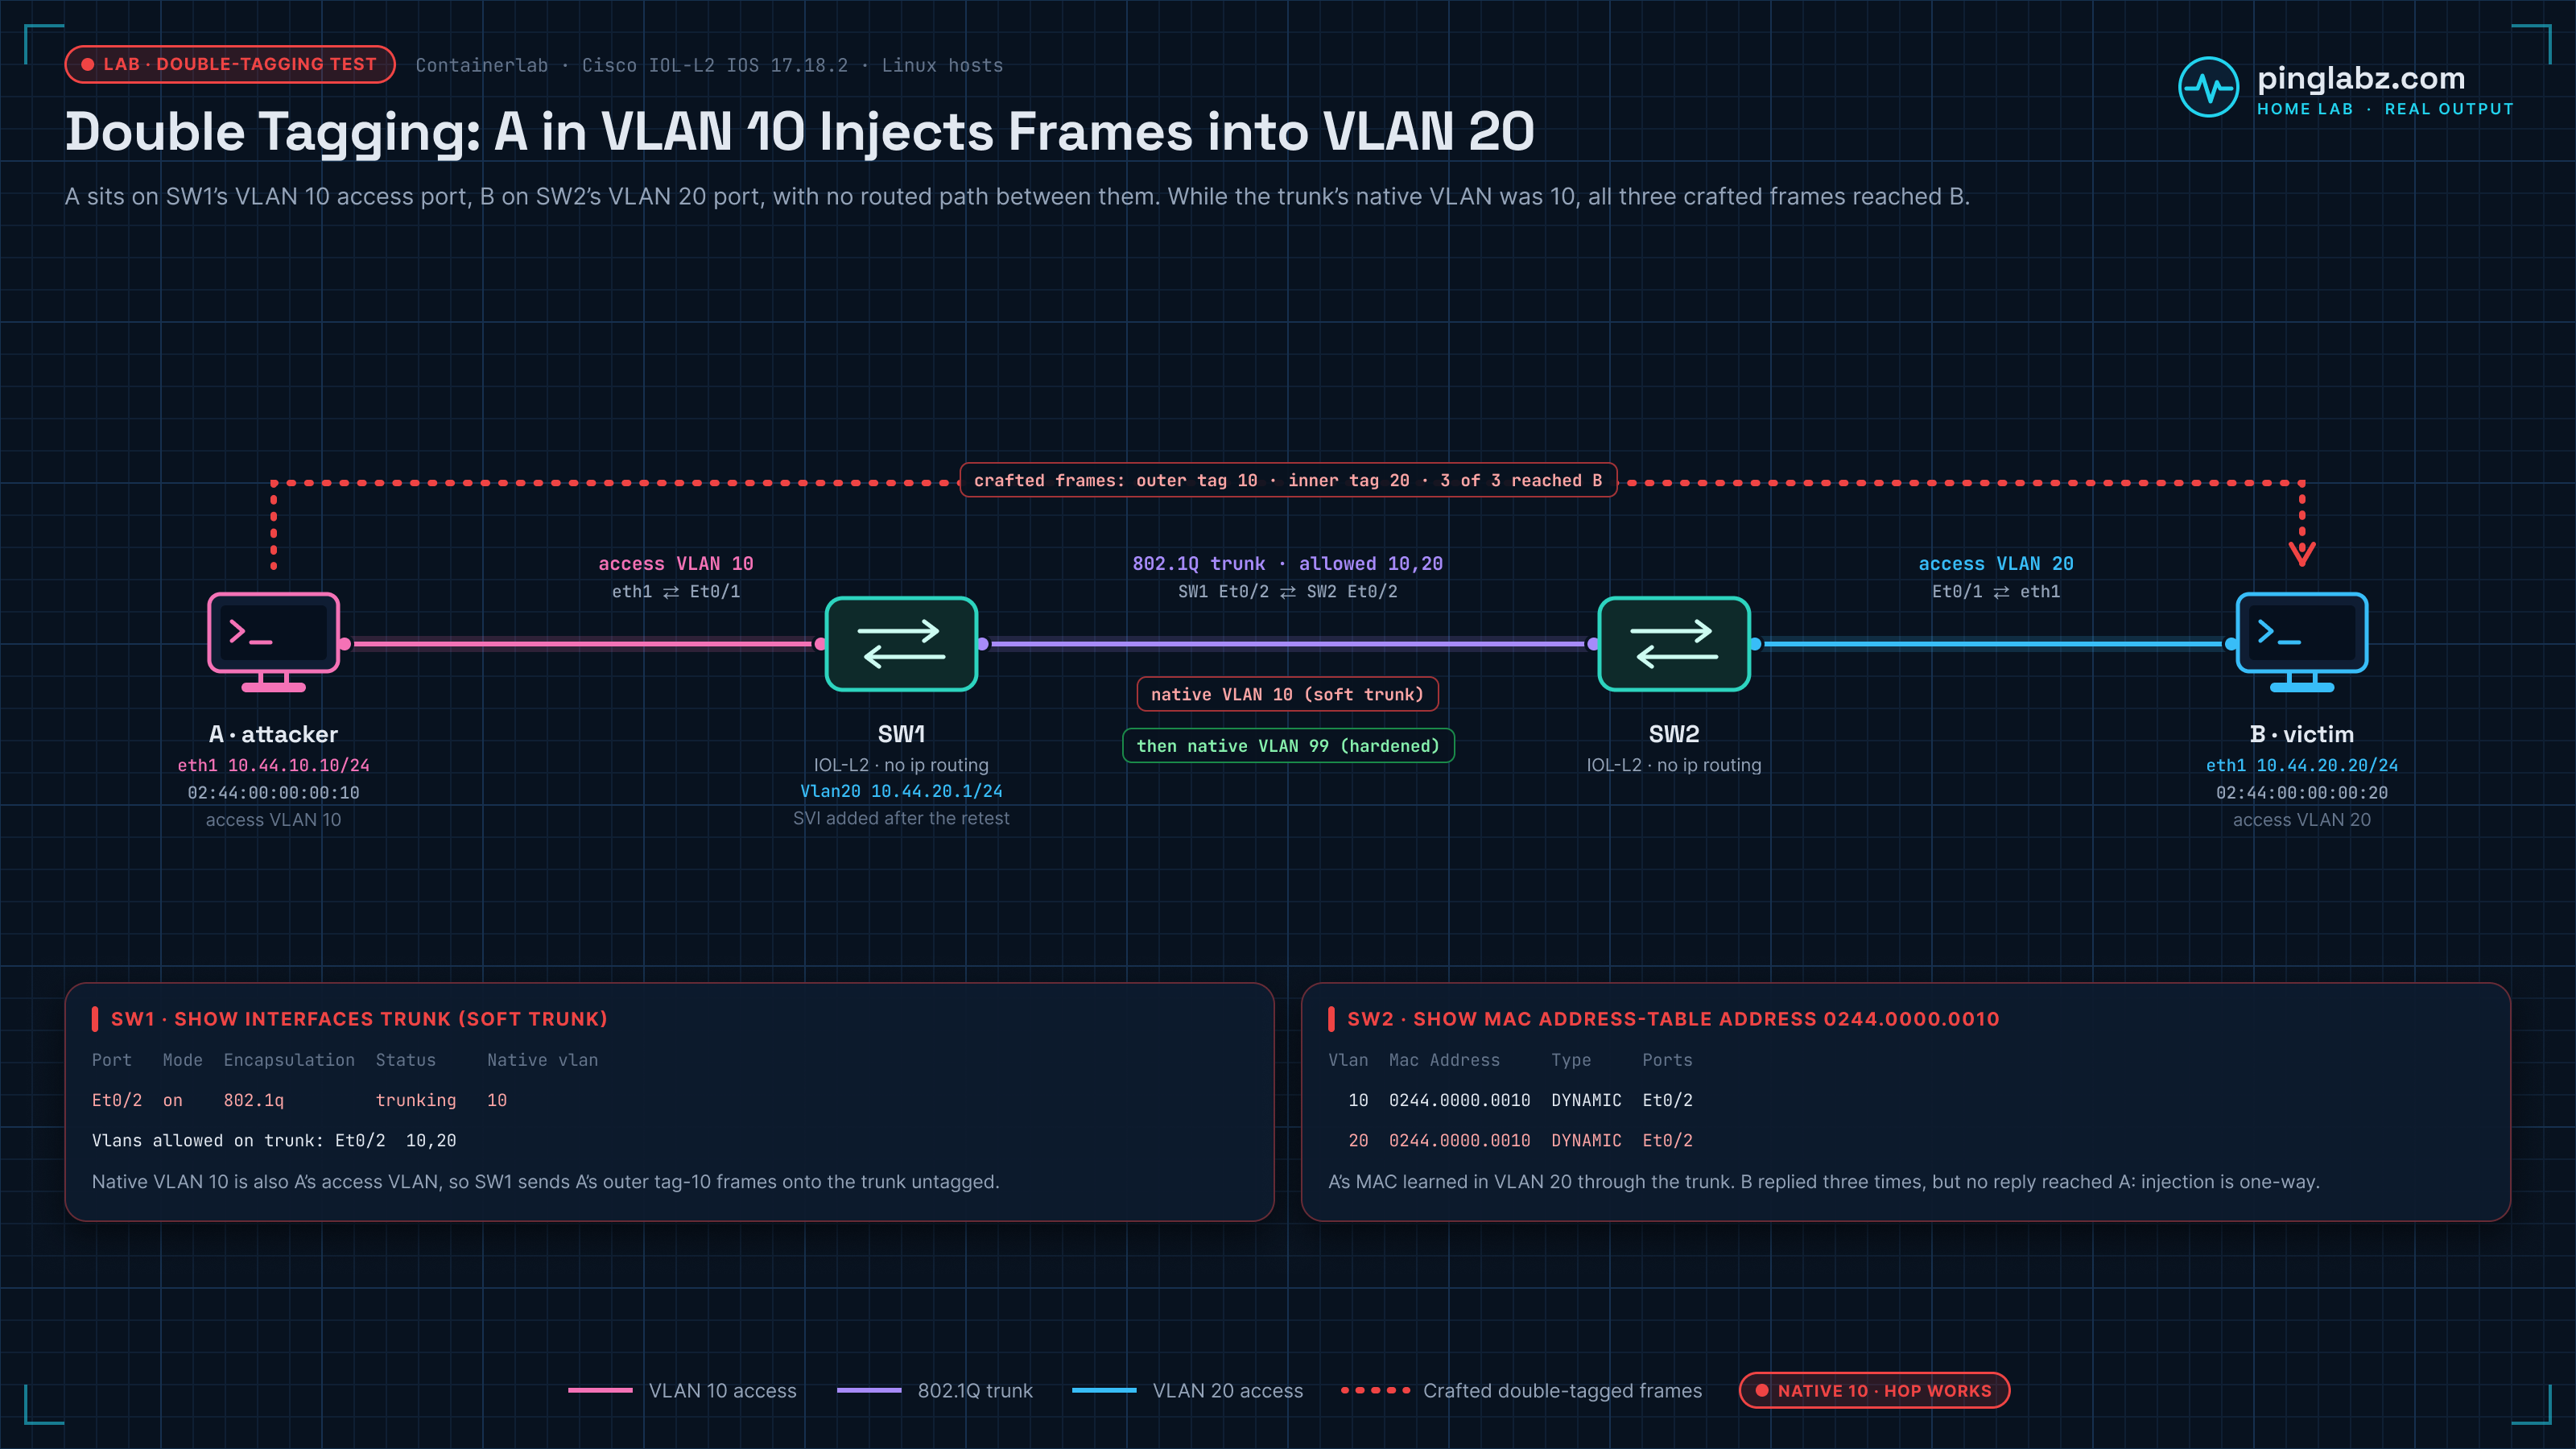
| Device or link | Interface | Data address / MAC | VLAN role |
|---|---|---|---|
| A, attacker | eth1 to SW1 Ethernet0/1 | 10.44.10.10/24, 02:44:00:00:00:10 | Access VLAN 10 |
| SW1 to SW2 | Ethernet0/2 at both ends | Layer 2 only | 802.1Q trunk; native 10 initially, then 99 |
| B, victim | eth1 to SW2 Ethernet0/1 | 10.44.20.20/24, 02:44:00:00:00:20 | Access VLAN 20 |
| Unused native VLAN | No host port or SVI | No data address | VLAN 99 after hardening |
| SW1 control SVI | Vlan20, added after the attack retest | 10.44.20.1/24 | Legitimate VLAN 20 reachability check |
Both switches had no ip routing. A and B each had a direct /32 route to the peer through eth1 and a permanent neighbor entry for the peer's MAC. That makes the ordinary ping test emit actual Ethernet frames toward the victim instead of failing at route lookup or ARP. It does not put the hosts in the same VLAN.
The soft configuration deliberately reused user VLAN 10 as the native VLAN at both trunk ends. Only VLANs 10 and 20 were allowed. SW1's running-configuration excerpt:
interface Ethernet0/1
 switchport access vlan 10
 switchport mode access
 spanning-tree portfast
!
interface Ethernet0/2
 switchport trunk encapsulation dot1q
 switchport trunk native vlan 10
 switchport trunk allowed vlan 10,20
 switchport mode trunk
SW2 used the same trunk configuration, with its host-facing Ethernet0/1 assigned to VLAN 20. On SW1, show interfaces trunk confirmed native VLAN 10 and both user VLANs forwarding:
Port           Mode             Encapsulation  Status        Native vlan
Et0/2          on               802.1q         trunking      10

Port           Vlans allowed on trunk
Et0/2          10,20

Port           Vlans allowed and active in management domain
Et0/2          10,20

Port           Vlans in spanning tree forwarding state and not pruned
Et0/2          10,20
The corresponding show interfaces Ethernet0/2 switchport excerpt made the exposure explicit: native VLAN 10, native tagging disabled, negotiation On.
Name: Et0/2
Switchport: Enabled
Administrative Mode: trunk
Operational Mode: trunk
Administrative Trunking Encapsulation: dot1q
Operational Trunking Encapsulation: dot1q
Negotiation of Trunking: On
Access Mode VLAN: 1 (default)
Trunking Native Mode VLAN: 10 (USERS)
Administrative Native VLAN tagging: disabled
An ordinary A-to-B ping still failed. In the settled baseline capture, all three requests appeared untagged at A and on the native-VLAN trunk, but none reached B. A's ping output:
PING 10.44.20.20 (10.44.20.20) from 10.44.10.10 eth1: 56(84) bytes of data.

--- 10.44.20.20 ping statistics ---
3 packets transmitted, 0 received, 100% packet loss, time 2030ms
Send the Double-Tagged Frames
The sender ran inside A and used a Python AF_PACKET raw socket bound to eth1. It constructed the Ethernet frame directly: destination B's MAC, source A's MAC, outer 0x8100 tag for VLAN 10, inner 0x8100 tag for VLAN 20, then IPv4 and an ICMP echo request. No VLAN subinterface was involved.
It sent three frames, sequences 1–3, half a second apart. Each carried ICMP identifier 17412 and payload PL-VLANHOP-AUTHORIZED-DOUBLE-TAG. The first send record below includes every byte; the remaining two send records are omitted.
seq=1 length=82 sha256=d5dfdedc27291c2d161d0e940d2483f4dd3a9601c5c67a2e2b0c33bde7ff7c30 hex=0244000000200244000000108100000a8100001408004500003c44040000400104480a2c0a0a0a2c141408003c6b44040001504c2d564c414e484f502d415554484f52495a45442d444f55424c452d544147
sent=82
The lab host captured A's eth1, SW1's trunk link (eth2, corresponding to Ethernet0/2), and B's eth1 simultaneously. Captures were stopped and flushed before decoding. The tcpdump -e -n -xx decodes below show Ethernet headers and raw hex, filtered for either host's MAC. Each excerpt shows sequence 1; sequences 2 and 3 followed the same path.
At A's access link, the 82-byte frame has both tags. 8100 000a is the outer VLAN 10 tag; 8100 0014 is the inner VLAN 20 tag.
05:57:02.123538 02:44:00:00:00:10 > 02:44:00:00:00:20, ethertype 802.1Q (0x8100), length 82: vlan 10, p 0, ethertype 802.1Q (0x8100), vlan 20, p 0, ethertype IPv4 (0x0800), 10.44.10.10 > 10.44.20.20: ICMP echo request, id 17412, seq 1, length 40
	0x0000:  0244 0000 0020 0244 0000 0010 8100 000a
	0x0010:  8100 0014 0800 4500 003c 4404 0000 4001
	0x0020:  0448 0a2c 0a0a 0a2c 1414 0800 3c6b 4404
	0x0030:  0001 504c 2d56 4c41 4e48 4f50 2d41 5554
	0x0040:  484f 5249 5a45 442d 444f 5542 4c45 2d54
	0x0050:  4147
On the trunk, the frame is four bytes shorter. The outer VLAN 10 tag has gone, leaving VLAN 20 as the tag SW2 reads. The captured bytes equal the original frame with exactly that outer tag removed.
05:57:02.124554 02:44:00:00:00:10 > 02:44:00:00:00:20, ethertype 802.1Q (0x8100), length 78: vlan 20, p 0, ethertype IPv4 (0x0800), 10.44.10.10 > 10.44.20.20: ICMP echo request, id 17412, seq 1, length 40
	0x0000:  0244 0000 0020 0244 0000 0010 8100 0014
	0x0010:  0800 4500 003c 4404 0000 4001 0448 0a2c
	0x0020:  0a0a 0a2c 1414 0800 3c6b 4404 0001 504c
	0x0030:  2d56 4c41 4e48 4f50 2d41 5554 484f 5249
	0x0040:  5a45 442d 444f 5542 4c45 2d54 4147
At B's access link, the remaining tag has also gone. The 74-byte untagged frame still has A's source MAC, the same IP addresses, ICMP identifier, sequence and payload.
05:57:02.125386 02:44:00:00:00:10 > 02:44:00:00:00:20, ethertype IPv4 (0x0800), length 74: 10.44.10.10 > 10.44.20.20: ICMP echo request, id 17412, seq 1, length 40
	0x0000:  0244 0000 0020 0244 0000 0010 0800 4500
	0x0010:  003c 4404 0000 4001 0448 0a2c 0a0a 0a2c
	0x0020:  1414 0800 3c6b 4404 0001 504c 2d56 4c41
	0x0030:  4e48 4f50 2d41 5554 484f 5249 5a45 442d
	0x0040:  444f 5542 4c45 2d54 4147
SW2's show mac address-table address 0244.0000.0010 corroborated the hop. It learned A's MAC in VLAN 20 through the trunk, alongside the existing VLAN 10 entry:
SW2# show mac address-table address 0244.0000.0010
show mac address-table address 0244.0000.0010
          Mac Address Table
-------------------------------------------

Vlan    Mac Address       Type        Ports
----    -----------       --------    -----
  10    0244.0000.0010    DYNAMIC     Et0/2
  20    0244.0000.0010    DYNAMIC     Et0/2
Total Mac Addresses for this criterion: 2
B received all three requests and generated three replies. Those replies crossed the trunk tagged VLAN 20, but none appeared at A's VLAN 10 access link. This was one-way packet injection, not a successful ping session.
Move the Native VLAN and Repeat the Send
On both switches, VLAN 99 was created as UNUSED_NATIVE, with no host access port or SVI. Both trunk ends were moved to native VLAN 99, the allowed list became 10,20,99, and switchport nonegotiate was applied to the trunk and host-facing access port. SW1's resulting interface configuration:
interface Ethernet0/1
 switchport access vlan 10
 switchport mode access
 switchport nonegotiate
 spanning-tree portfast
!
interface Ethernet0/2
 switchport trunk encapsulation dot1q
 switchport trunk native vlan 99
 switchport trunk allowed vlan 10,20,99
 switchport mode trunk
 switchport nonegotiate
SW2 kept its access VLAN 20 and received the same trunk changes. VLANs 10 and 20 remained allowed, so removing the victim VLAN from the trunk cannot explain the failed retest. For the change procedure, see changing the native VLAN on Cisco switches.
Before repeating the send, the lab cleared old dynamic MAC entries and checked that VLANs 10 and 20 had returned to spanning-tree forwarding. Earlier capture windows showed only one of three requests on the trunk, consistent with spanning-tree transition timing. Those windows alone would make a poor security verdict. The settled SW2 show interfaces trunk output was:
Port           Mode             Encapsulation  Status        Native vlan
Et0/2          on               802.1q         trunking      99

Port           Vlans allowed on trunk
Et0/2          10,20,99

Port           Vlans allowed and active in management domain
Et0/2          10,20,99

Port           Vlans in spanning tree forwarding state and not pruned
Et0/2          10,20,99
The hardened SW1 trunk's switchport output confirmed native VLAN 99 and negotiation Off. Native tagging was still disabled:
Name: Et0/2
Switchport: Enabled
Administrative Mode: trunk
Operational Mode: trunk
Administrative Trunking Encapsulation: dot1q
Operational Trunking Encapsulation: dot1q
Negotiation of Trunking: Off
Access Mode VLAN: 1 (default)
Trunking Native Mode VLAN: 99 (UNUSED_NATIVE)
Administrative Native VLAN tagging: disabled
The sender replayed the exact same three frames, with matching SHA256 hashes. At A's access link, sequence 1 was still double-tagged:
05:58:12.355019 02:44:00:00:00:10 > 02:44:00:00:00:20, ethertype 802.1Q (0x8100), length 82: vlan 10, p 0, ethertype 802.1Q (0x8100), vlan 20, p 0, ethertype IPv4 (0x0800), 10.44.10.10 > 10.44.20.20: ICMP echo request, id 17412, seq 1, length 40
	0x0000:  0244 0000 0020 0244 0000 0010 8100 000a
	0x0010:  8100 0014 0800 4500 003c 4404 0000 4001
	0x0020:  0448 0a2c 0a0a 0a2c 1414 0800 3c6b 4404
	0x0030:  0001 504c 2d56 4c41 4e48 4f50 2d41 5554
	0x0040:  484f 5249 5a45 442d 444f 5542 4c45 2d54
	0x0050:  4147
This time the trunk retained both tags and all 82 bytes. VLAN 10 was no longer native, so the outer tag remained visible to SW2:
05:58:12.355987 02:44:00:00:00:10 > 02:44:00:00:00:20, ethertype 802.1Q (0x8100), length 82: vlan 10, p 0, ethertype 802.1Q (0x8100), vlan 20, p 0, ethertype IPv4 (0x0800), 10.44.10.10 > 10.44.20.20: ICMP echo request, id 17412, seq 1, length 40
	0x0000:  0244 0000 0020 0244 0000 0010 8100 000a
	0x0010:  8100 0014 0800 4500 003c 4404 0000 4001
	0x0020:  0448 0a2c 0a0a 0a2c 1414 0800 3c6b 4404
	0x0030:  0001 504c 2d56 4c41 4e48 4f50 2d41 5554
	0x0040:  484f 5249 5a45 442d 444f 5542 4c45 2d54
	0x0050:  4147
All three double-tagged requests appeared on the trunk. The host-MAC-filtered decode at B contained no matching frames, and no probe replies appeared. After the replay, SW2's lookup for A's MAC showed only VLAN 10:
SW2# show mac address-table address 0244.0000.0010
show mac address-table address 0244.0000.0010
          Mac Address Table
-------------------------------------------

Vlan    Mac Address       Type        Ports
----    -----------       --------    -----
  10    0244.0000.0010    DYNAMIC     Et0/2
Total Mac Addresses for this criterion: 1
The optional global vlan dot1q tag native command was not applied or tested. Native tagging stayed disabled throughout, so this comparison shows the effect of moving the native VLAN. Check native-tagging support separately on the image you use.
Check the Victim and Trunk Still Work
After the failed replay, a VLAN 20 SVI on SW1 supplied legitimate traffic across the same trunk to B. IPv4 routing stayed disabled, and no VLAN 10 SVI was added. The switch CLI reported two of three pings successful:
SW1# ping 10.44.20.20 source Vlan20 repeat 3 timeout 1
ping 10.44.20.20 source Vlan20 repeat 3 timeout 1
Type escape sequence to abort.
Sending 3, 100-byte ICMP Echos to 10.44.20.20, timeout is 1 seconds:
Packet sent with a source address of 10.44.20.1
.!!
Success rate is 66 percent (2/3), round-trip min/avg/max = 2/2/3 ms
The captures recorded all three control requests and all three replies at B and on the trunk, tagged VLAN 20 on the trunk and untagged at B. Keep that wire result distinct from the CLI's 2/3 counter. Both show that the hardened trunk could still carry legitimate VLAN 20 traffic.
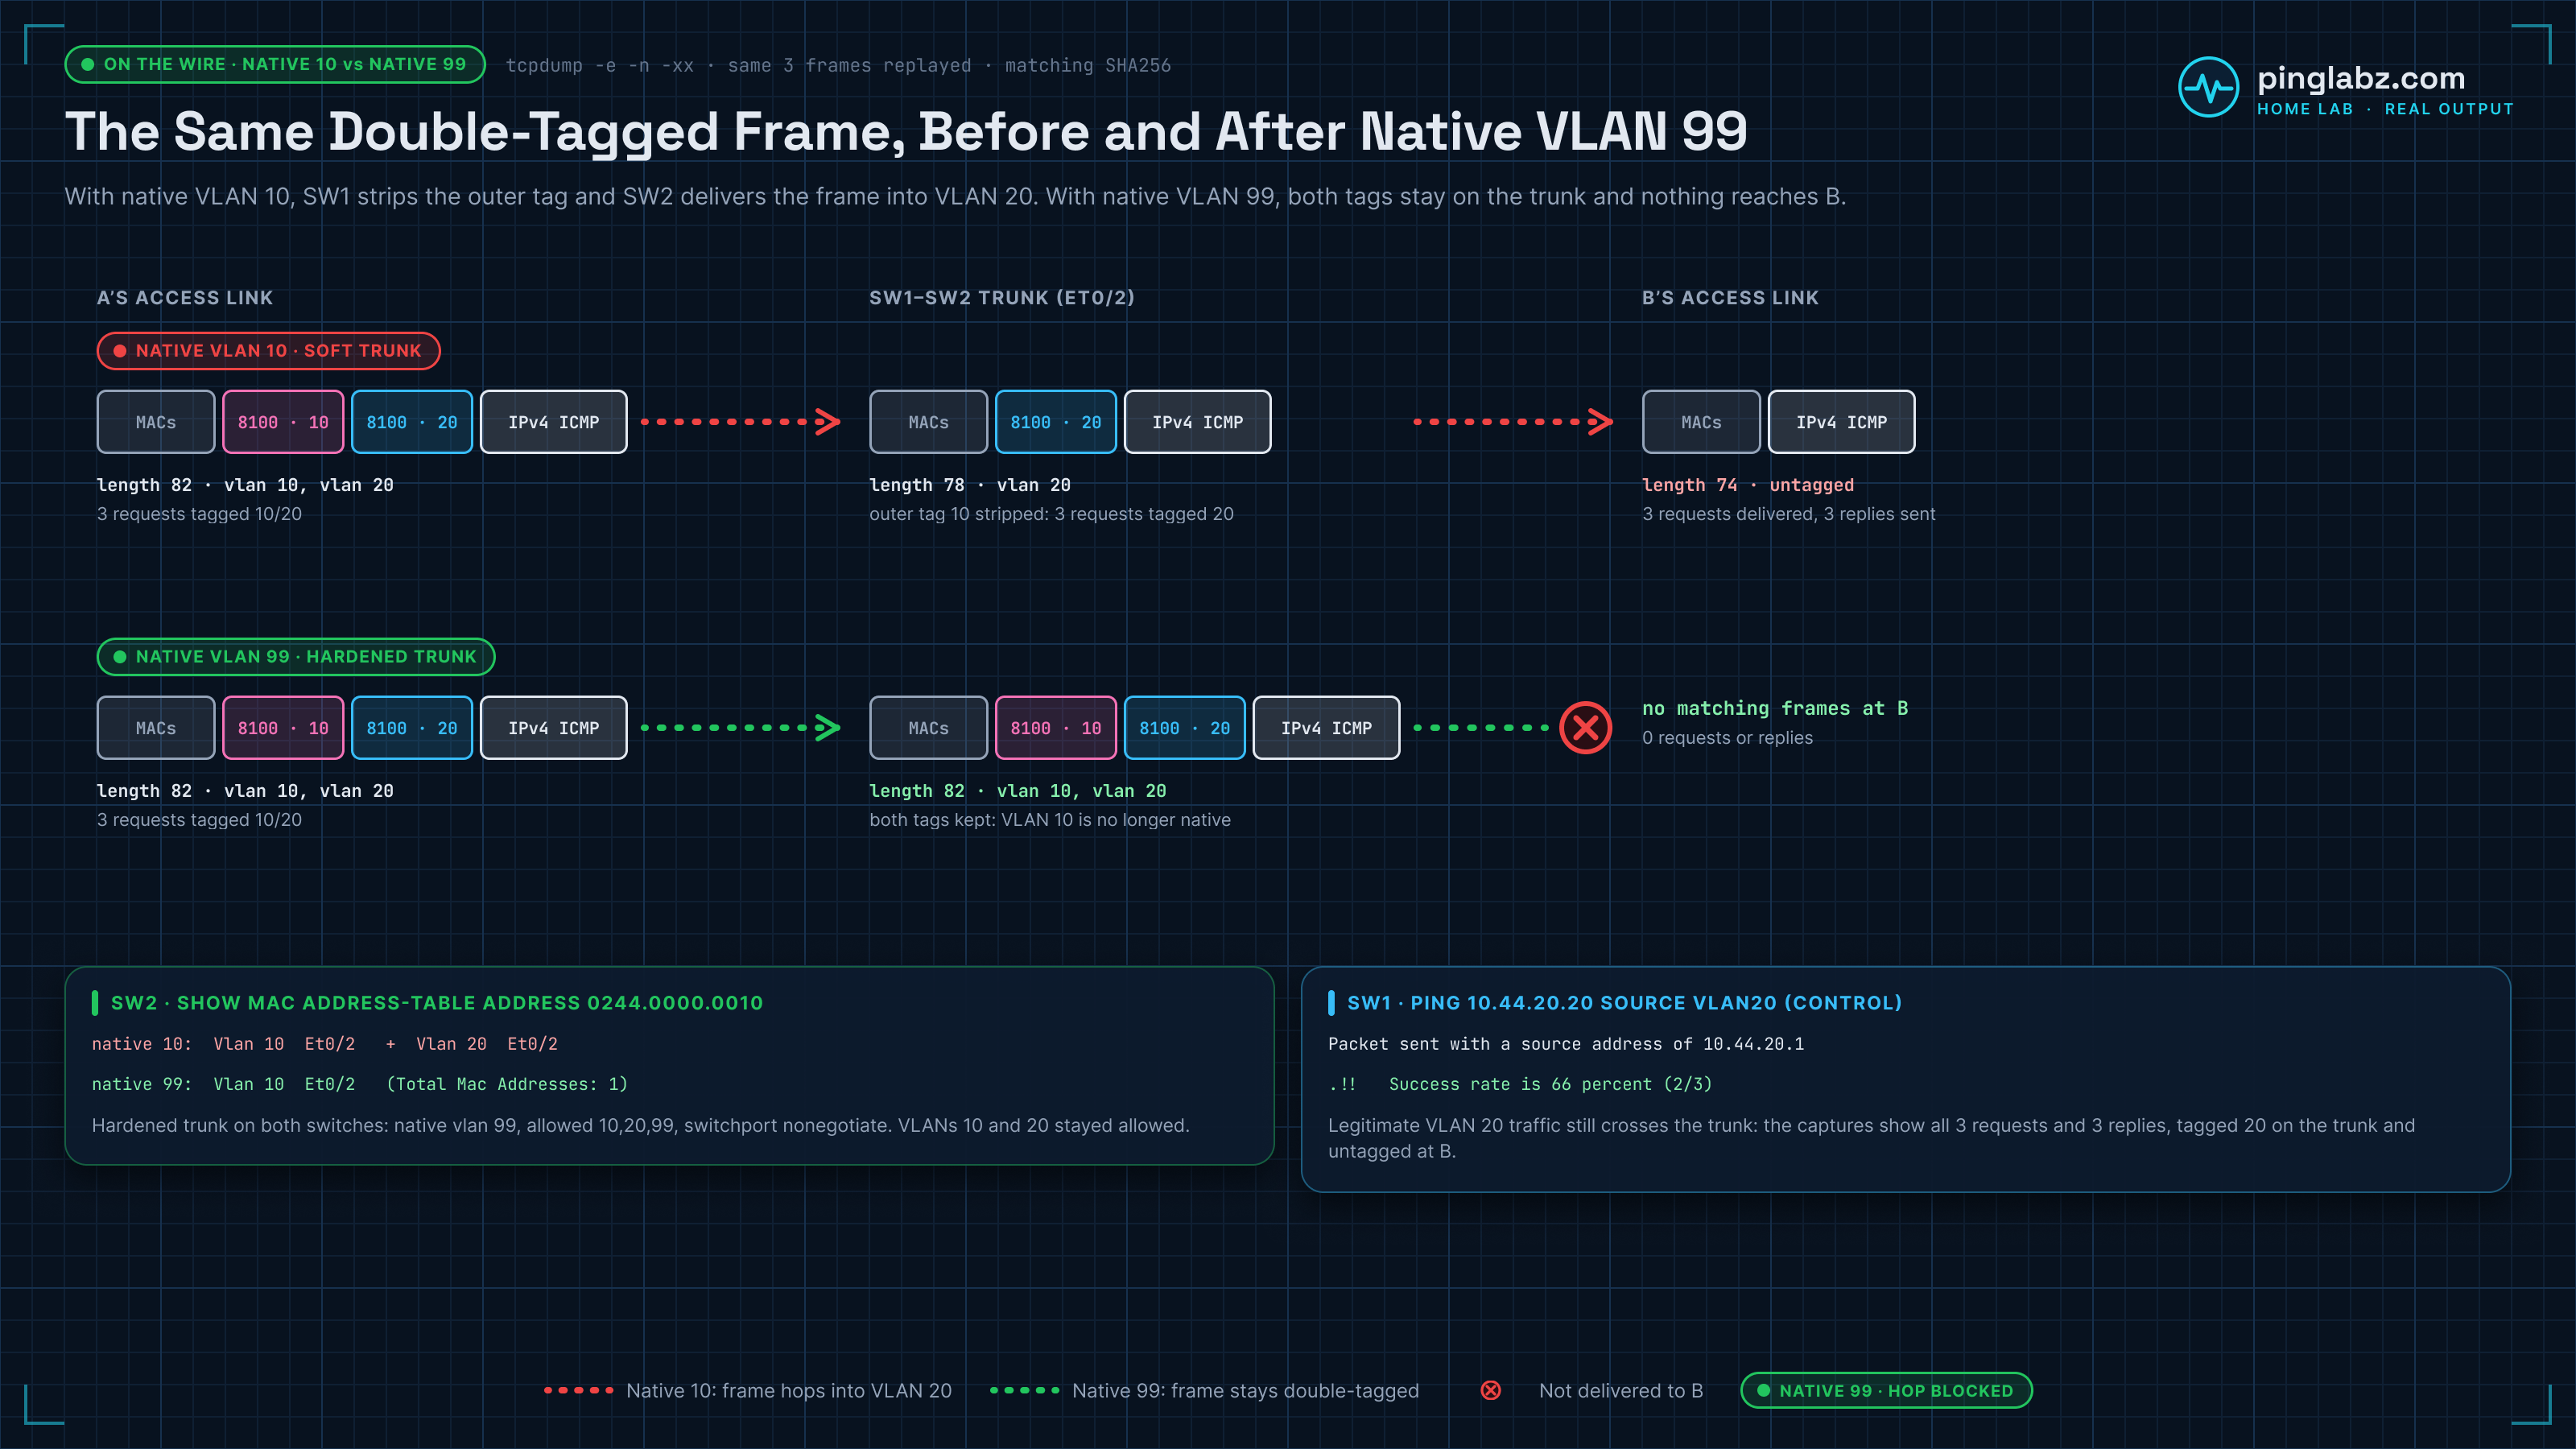
| Settled test | A access link | SW1–SW2 trunk | B access link |
|---|---|---|---|
| Ordinary ping, native 10 | 3 untagged requests | 3 untagged requests in native VLAN 10 | 0 requests |
| Crafted send, native 10 | 3 requests tagged 10/20 | 3 requests tagged 20 | 3 untagged requests and 3 replies |
| Same crafted send, native 99 | 3 requests tagged 10/20 | 3 requests still tagged 10/20 | 0 requests or replies |
| Legitimate VLAN 20 control, native 99 | No ICMP | 3 VLAN 20 requests and 3 replies | 3 untagged requests and 3 replies |
| Ordinary A-to-B ping, native 99 | 3 untagged requests | 3 requests tagged 10 | 0 requests |
Moving the native VLAN did not break the trunk or shut down B. It kept the attacker's outer VLAN 10 tag on the wire, so SW2 no longer treated the frame as VLAN 20 traffic. The tagged and untagged VLAN guide explains the normal tag changes that these captures put to the test.
How to Test (in a Lab)
The Containerlab section above gives a measured double-tagging example: capture both access links and the trunk, check MAC learning, then replay identical frames after hardening. Use the victim capture to judge injection; a failed ping at the attacker can hide successful one-way delivery.
If you want to verify your switches are not vulnerable, the testing tools are well-known but only run them in a lab you own:
- Yersinia. Open-source Layer 2 attack framework. Has DTP and double-tagging modules.
- Scapy. Python framework that can craft arbitrary 802.1Q-tagged frames for the double-tagging attack.
The acceptable lab pattern: build a topology with two switches and three hosts (one in each VLAN, plus an attacker), run the attack against an unhardened configuration, observe the attacker reaching the target VLAN, apply the hardening, and confirm the attack now fails. This is part of every CCNP Security and Cisco SECURE lab.
Why VLAN Hopping Still Matters in 2026
The mitigations have been documented for over twenty years. The attacks are taught in every CCNA Security textbook. And yet network audits keep finding production trunks with the default native VLAN of 1, access ports with default DTP enabled, and management VLANs that share trunk access with everything else.
Three reasons:
- Defaults are sticky. Many switch deployments inherit configurations that pre-date hardening guides. Re-templating a deployed network is hard.
- Access is assumed. If your physical security is strong, the attacker cannot get to a wall jack. But voice phones, conference rooms, BYOD, and lab environments all undermine this assumption.
- Virtualization extends the attack surface. A VM on a vSwitch with default VLAN settings can perform the same attacks as a physical attacker. The double-tagging vector reaches into virtual networks too.
The fix is short, well-understood, and free. The PingLabz position: every trunk in 2026 should have switchport nonegotiate, a non-default native VLAN, and explicit allowed VLAN lists. If your network does not, this is the lowest-effort security improvement you can make today.
Summary
VLAN hopping is two attacks: switch spoofing via DTP and double tagging via the native VLAN. Both let an attacker bypass Layer 2 isolation and reach VLANs they should not be on. Both are defeated by short configurations: switchport nonegotiate on every port, native VLAN moved off VLAN 1, and either vlan dot1q tag native globally or aggressive native-VLAN hygiene on trunks.
If your network is running default Cisco settings, you are vulnerable. The fix takes minutes; the consequence of not fixing it is real, recurrent, and exploitable. Bookmark the VLAN cluster pillar for the full operational picture, and review the broader Layer 2 hardening checklist above on every audit.